SharePoint Embedded Explained

Work in progress…

SharePoint Embedded can be confusing at first because it uses SharePoint technology, but it does not work like the SharePoint sites most Microsoft 365 administrators are familiar with.

Instead of creating a traditional SharePoint site and asking users to work with documents there, SharePoint Embedded allows an application to use Microsoft 365 as its document storage platform. The application controls the user experience, while SharePoint provides the underlying content storage, security, compliance, and Microsoft 365 integration.

This article explains SharePoint Embedded from a Microsoft 365 administrator and engineer perspective, including its architecture, containers, permissions, Microsoft Graph integration, governance, and practical use cases.

How much is SharePoint Embedded

First of all – as per Microsoft – “The SharePoint Embedded partition doesn’t count against Microsoft 365 storage entitlements; it’s billed separately through an Azure subscription on a pay-as-you-go, metered model based on storage and API usage. See Choose a billing model and Billing meters.”

So SharePoint Embedded is not free and is not included with regular Microsoft 365 licenses.

You can try it before buy it using Trial container type to explore SharePoint Embedded development without linking an Azure billing profile, and it’s done via vs code or Graph API, there is no GUI.

SharePoint Embedded Admin Roles and Permissions

Second – there is a dedicated “SharePoint Embedded Administrator” role required to administer SharePoint Embedded. Regular “SharePoint Administrator” role does not administer SharePoint Embedded apps or containers.

Administering happens under SharePoint admin center, and here is what a SharePoint Admin plus SharePoint Embedded Admin can see (if you got just a SharePoint Embedded Admin role – the only you’d see is what circled red – SharePoint Embedded Apps and Containers).
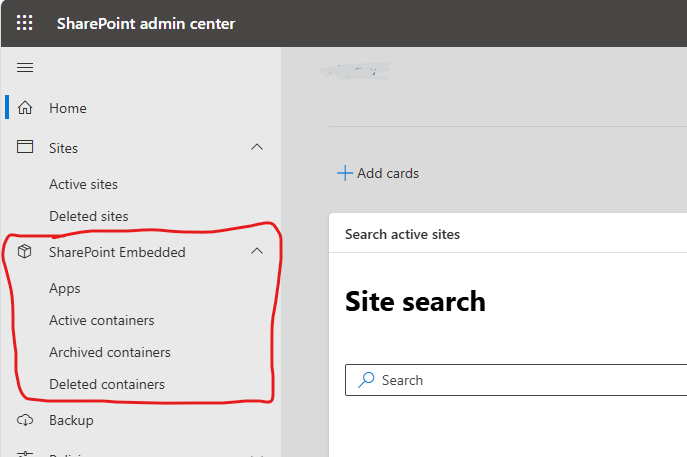
With respect to app registrations

FileStorageContainerType.Manage.All delegated permission (app-only access isn’t supported):
– Allows the application to manage file storage container types on behalf of the signed in user. The user must be a SharePoint Embedded Admin or Global Admin.
– Allows to create a trial container type (No admin role required for the calling user)

SharePoint Embedded Admin Roles and Permissions

SharePoint Embedded App Users

User of an application that under the hood uses SharePoint Embedded functionality:

  • must have an identity in tenant (users accessing SharePoint Embedded containers authenticate through Microsoft Entra ID): either a Member or a Guest brought into the tenant through Entra B2B
  • Does not need a Microsoft 365 license (however, if the application also exposes other Microsoft 365 services, those services can have their own licensing requirements)

SharePoint Embedded Ownership

What Does the SharePoint Admin Actually Manage

The SharePoint team (especially in large environments with separated responsibilities) probably does very little provisioning for SharePoint Embedded. Whoever needs SharePoint embedded – deal with IdM to register an application, billing to establish billing, and the application owns creation and day-to-day use of containers through Microsoft Graph. Microsoft describes a container as normally managed by the application, while administrators handle governance operations.

So the SharePoint admin/team still has an important role: platform governance, visibility, lifecycle management, configuration, and troubleshooting/escalation.

Specifically:

Governance: lifecycle, SharePoint controls, compliance integration.
Operations: administrative actions, archive/restore/delete, configuration changes.
Support: troubleshooting SharePoint Embedded containers and determining whether an incident is SharePoint, application, identity, or another platform.

SharePoint Embedded Governance

SharePoint Embedded governance is the management of the SharePoint-specific controls and lifecycle of content stored by applications, rather than governance of the applications themselves.

SharePoint administrators should establish governance around:

1. Container lifecycle
How containers are archived, restored, deleted and permanently removed.

2. Administrative intervention
When SharePoint administrators are allowed to modify containers outside the application.

3. Security and compliance integration
How SharePoint Embedded content participates in existing sensitivity, retention, DLP, eDiscovery, audit and access-control processes.

4. Application retirement
How Embedded content is discovered and dispositioned when the enterprise application using it is retired.

5. Support and escalation
What the SharePoint team investigates and where the boundary lies between SharePoint, the application, Entra, Purview and other enterprise teams.

References

Orphaned Users Clean Up in Microsoft 365 SharePoint

Cleaning Up Orphaned Users in Microsoft 365 SharePoint to Prevent User ID Mismatch Issues

What Is an Orphaned User in SharePoint?

To understand orphaned users, it helps to look at how SharePoint tracks user data. When a user account is created in Microsoft Entra ID and assigned a SharePoint license, they gain access to SharePoint sites.

Every SharePoint site maintains a User Information List—a local cache where SharePoint stores essential user metadata, such as display names, job titles, and email addresses. When a user account is eventually deleted from Entra ID, their data is not automatically purged from SharePoint. This is intentional: SharePoint preserves user metadata for historical integrity, allowing team members to see who created or updated a document.

An orphaned user is a user record whose metadata remains cached within a SharePoint site’s User Information List, even though the corresponding identity no longer exists in Entra ID. This phenomenon occurs across every SharePoint site the user interacted with during their tenure.

The User ID Mismatch Issue

While preserving metadata is useful for auditing and history, it sets the stage for the User ID Mismatch issue.

This scenario typically happens when a new account in EntraId is created with the exact same User Principal Name (UPN) as a former worker, for instance in cases:

  • An employee leaves and is later rehired
  • A contractor is converted to a full-time employee
  • A new employee is onboarded who happens to share the same name

When the new account is created in Entra ID and receives the same UPN it is always assigned a brand-new, unique internal object ID. When this user attempts to access SharePoint, a collision occurs:

  1. Security by Design: SharePoint checks its local User Information List and finds an existing entry for that UPN, but the internal account IDs do not match. SharePoint correctly denies access, treating the incoming user as an unrecognized identity.
  2. The Access Block Bug: The real problem arises when a site administrator attempts to explicitly grant access. Even with admin approval, SharePoint fails to update the reference to the new account ID because the old legacy record occupies the database entry. SharePoint continues blocking access without returning a clear error message.

Microsoft acknowledges this limitation: the legacy user record must be completely removed from the site’s User Information List before the new user can be granted access.

Why Microsoft’s Native Solution Falls Short at Scale

While Microsoft provides a standard resolution—deleting the old legacy ID from the site—the fix is GUI-based and designed strictly on a single-site, single-user basis.

In an enterprise environment, this creates severe operational hurdles:

  • Tenant-Wide Scope: An average employee might access dozens or hundreds of sites throughout their organizational tenure. Fixing a mismatch requires applying Microsoft’s fix across every single site the user touched. Though we can do the same with PowerShell, there is a second problem –
  • Lack of Out-of-the-Box Reporting: There is no native report that displays all occurrences of a legacy account across all SharePoint sites in a tenant. While a brute-force PowerShell script can scan a tenant, doing so in medium-to-large organizations is resource-intensive and exceptionally slow.
  • User Frustration: The error presents silently. SharePoint appears to work normally, but access fails. When a user contacts a site owner who approves access yet nothing changes, it creates confusion. Once resolved on one site, the user frequently hits the exact same issue on other sites, assuming the entire problem was fixed globally.

Strategic Approaches: Prevention vs. Cleanup

To effectively manage User ID Mismatch issues, I think organizations should generally look at three distinct activities:

1. Proactive Prevention (“Stop Tickets”)

For just onboarded users (incoming accounts), you can proactively check newly created Entra ID accounts against historical UPNs. If a match is found, you can scan and clean up potential orphaned records across SharePoint sites before the user ever encounters an access block.

2. Automated Offboarding (“Stop Bleeding”)

At the exact moment a user account is disabled or deleted from Entra ID, an automated routine can sweep SharePoint sites to remove the newly orphaned user metadata. Stopping the bleeding at the point of departure prevents new orphaned records from accumulating.

3. Historical Cleanup of Existing Orphaned Users

For mature tenants that have been active for years, orphaned users have already accumulated in massive numbers. Estimating roughly, in a mature tenant (e.g., 10 years old), the number of orphaned user records can scale to rival the number of active users in Entra ID. (see How Many Orphaned Users Do You Have in SharePoint?)

Cleaning up existing orphaned users tenant-wide is the cornerstone of resolving widespread User ID Mismatch friction.

Technical Cleanup Strategy for Large Organizations

While smaller tenants with a few dozen sites can rely on a simple brute-force scan across every site, brute-force scanning for large enterprises with 100,000+ sites is impossible. But one of the approaches I came up and effectively use in my tenants I support is below.

The goal here isn’t an exhaustive, 100% tenant-wide purge—it’s about capturing the low-hanging fruit. By applying a targeted 80/20 strategy, you can eliminate a massive portion of the organization’s User ID Mismatch issues with relatively minimal effort:

Step 1: Target High-Population Sites First

Instead of scanning 100,000 sites, target the top ~20 high-population sites where most organization members have visited. This typically includes The main Corporate Intranet / Portal, Company-wide news sites, Sites tied to widely joined public Teams or organization-wide Viva Engage (Yammer) communities.

Focusing on these key high-traffic sites allows us to proactively eliminate a massive portion of cached orphaned user records with a manageable level of effort.

Real-world data shows why this is so effective: when analyzing onboarded users who experienced UPN reuse, legacy user records are rarely spread across hundreds of niche sites. Instead, for the majority of users, their legacy access—and thus their cached data—was confined to just a handful of company-wide, high-population sites that everyone visits. Clearing these top sites eliminates the bulk of potential user ID mismatch landmines before users ever hit them.

Step 2: Query the User Information List Directly

Avoid using Get-PnPUser on large sites, as it takes an impractically long time to run. Instead, query the underlying Site User Information List directly to fetch all items. Even for sites with hundreds of thousands of cached users, this query completes within a few minutes. Convert these list items into usable user objects in memory.

Step 3: Fast Matching via Entra ID Hash Tables

  1. Retrieve all active users from Microsoft Entra ID.
  2. Build an in-memory Hash Table of active Entra ID accounts indexed by UPN.
  3. Iterate through the SharePoint site users and check their existence against the Entra ID hash table. Because hash table lookups occur in O(1) time, identifying all orphaned users on a site takes only minutes.

Step 4: Parallelized Deletion

Running Remove-PnPUser sequentially across thousands of orphaned users takes roughly 1 second per user—meaning a single site could take days or weeks.

To bypass this bottleneck, leverage PowerShell Parallelism (e.g., ForEach-Object -Parallel). Executing user deletions concurrently reduces the processing time for ~100,000 orphaned users down to approximately one hour.

Summary Workflow

  1. Identify top 20 high-traffic corporate sites.
  2. Fetch site users via the hidden User Information List (bypassing Get-PnPUser).
  3. Compare site users against an active Entra ID Hash Table.
  4. Purge identified orphaned records using PowerShell parallel execution.

Stay tuned for an upcoming post where I will share the exact PowerShell script and code samples implementing this optimized workflow!

References

How to Audit SharePoint Permissions Before Enabling Copilot

Microsoft 365 Copilot respects the permissions that already exist in SharePoint. This means that preparing SharePoint for Copilot is not only about enabling new technology. It is also an opportunity to understand who currently has access to what, identify potential oversharing, and clean up permissions that may no longer make business sense. This article will walk through the main areas that should be reviewed as part of a SharePoint permission audit before a broader Copilot rollout.

Topics covered in this article:

  • Building an inventory of SharePoint sites
  • Identifying and prioritizing sensitive or high-risk sites
  • Reviewing site owners and administrators
  • Identifying sites with broad access
  • Reviewing SharePoint and Microsoft 365 group membership
  • Finding direct user permissions
  • Identifying broken permission inheritance and unique permissions
  • Reviewing sharing links
  • Reviewing guest and external access
  • Identifying stale or outdated permissions
  • Detecting common oversharing patterns
  • Prioritizing permission findings based on risk
  • Remediating permission issues before enabling Copilot
  • Establishing ongoing permission monitoring and governance

wip…

Microsoft 365 Search and enterprise knowledge

This builds directly on my search expertise while connecting it to the newer AI experiences. Microsoft’s current direction places SharePoint knowledge at the center of Copilot and agent experiences.

Articles TBD:

  • Why a SharePoint Document Doesn’t Appear in Microsoft Search
  • Why Copilot Cannot Find a Document That a User Can Open
  • How Permissions, Indexing, and Sensitivity Labels Affect Search
  • How to Troubleshoot Microsoft Search Across SharePoint and Teams
  • How to Prepare SharePoint Content for Better AI Retrieval
  • SharePoint Metadata vs. File Names: Which Helps Enterprise Search More?

Microsoft Purview, security, and compliance

Microsoft’s Copilot controls increasingly connect data governance, information protection, auditing, and AI risk management.

Articles TBD:

  • How Sensitivity Labels Affect SharePoint, Teams, and Microsoft 365 Groups
  • How to Audit Who Accessed Sensitive SharePoint Content
  • How to Find SharePoint Sites That Violate Your Governance Policies
  • How to Investigate Copilot Activity Using Microsoft Purview Audit
  • DLP Policies for Copilot: Practical Scenarios and Limitations
  • Microsoft 365 E3 vs. E5: Which Governance Capabilities Do You Actually Need?

Audience: IT governance, security, and compliance administrators.

Microsoft Teams governance and lifecycle

Teams combines collaboration, Microsoft 365 Groups, SharePoint sites, memberships, and lifecycle management. That creates many practical problems for administrators.

Articles TBD:

  • How to Find Teams With No Owners or Inactive Members
  • What Happens to the SharePoint Site When a Team Is Archived?
  • How to Report on Teams, Channels, Owners, and Memberships
  • How to Find Orphaned Microsoft 365 Groups
  • How to Design a Microsoft Teams Expiration and Renewal Process
  • How to Audit External Users Across Teams and SharePoint

Microsoft Graph and PowerShell automation

Administrators often need repeatable reporting and remediation beyond what a portal can conveniently provide.

Articles TBD:

  • How to Find Every SharePoint Site Without an Owner
  • How to Build a Microsoft 365 Governance Report With Microsoft Graph
  • How to Detect and Report Permission Changes Across SharePoint
  • App-Only Authentication vs. Managed Identity for Microsoft 365 Automation
  • How to Rotate Certificates Used by Microsoft 365 Automation Without Downtime
  • How to Build Reliable, Auditable PowerShell Automation for Microsoft 365

Audience: Microsoft 365 engineers who need to solve problems at tenant scale.

Managing and governing AI agents

Microsoft is expanding agent management, including controls for agent availability, access, and usage. SharePoint administrators now have new agent-related governance capabilities to understand.

Articles TBD:

  • How to Inventory Copilot Agents Across a Microsoft 365 Tenant
  • How SharePoint Permissions Affect AI Agent Responses
  • Who Can Create and Publish Copilot Agents? An Administrator’s Guide
  • How to Audit Which Agents Can Access Your SharePoint Content
  • SharePoint Agents vs. Copilot Studio Agents: What Administrators Need to Know

Copilot readiness and SharePoint governance

Organizations need to make existing content safe and useful for AI without accidentally exposing sensitive information. Microsoft explicitly recommends addressing oversharing, inactive sites, and governance before relying on Copilot.

Audience: Microsoft 365 administrators, architects, security teams.

Articles TBD:

  • How to Find SharePoint Sites That Are Overshared Before Enabling Copilot
  • SharePoint Copilot Readiness Checklist for Enterprise Administrators
  • How to Identify and Remediate Sites With Broken Permission Governance
  • Restricted Content Discovery vs. Restricted Access Control: What’s the Difference?
  • How to Build a SharePoint Copilot Readiness Report With PowerShell

User Id Mismatch in OneDrive scenario

By “User Id Mismatch in OneDrive scenario” I mean user’s own OneDrive, not somebody’s else OD. Somebody’s else OneDrive site can be fixed the same way as any other site – remove the legacy user, add the new user. Simple. But when a user is experiencing User Id Mismatch with their own OneDrive site – it’s a separate scenario.

Why such cases exist? How can a user cannot access their own OneDrive site because of User Id Mismatch? It happens when an account is deleted and then recreated with the same UPN within a short period of time. E.g. contractor converted to employee or user returned earlier from a short-term leave.
The thing is OneDrive sites are not deleted immediately when Entra Id account is deleted. There is a retention period (Customizable. 30 days by default. Actually there are two processes – archiving and retention here is the review – OneDrive Site Lifecycle – 93-Day Unlicensed Archiving vs Standard Retention).

Typical workflow that leads to a User Id Mismatch in OneDrive case

  1. User leaves organization by some reason, here is what usually happens
  • User account is disabled
  • Permissions are removed
  • Licenses are removed -> OD archival process is triggered
  • User account is deleted -> retention process starts

2. User returns to organization after his Entra Id account is deleted, but before his OneDrive site is deleted, here is what usually happens

  • A new Entra Id account is created with the same UPN
  • User assumes that he/she still should have all his OD files in place
  • what actually happens with respect to OneDrive
    • case 1: a new OneDrive is created – user claims that all OneDrive documents are missing
    • case 2: an existing OneDrive associates with the new user account – user “looses” access to own OD

What do we do to resolve a User Id Mismatch in OneDrive scenario

Case 1: a new OneDrive is created – user claims that all OneDrive documents are missing.
This case in terms of tech resolution is similar to the regular User Id Mismatch scenario. The only we need is to explain the issue to the user and engage user with data migration. Admin’s actions:

  • ensure that it’s the same person
  • provide access for the new Id to the old OD
  • inform user that the old OD will be deleted automatically, so if any information is needed – user should move data out of old OneDrive site

Case 2: an existing OneDrive associates with the new user account – user “looses” access to own OD.
This case is different, and the regular regular User Id Mismatch resolution workflow won’t work. The reason – we cannot remove a single primary owner from a site. So Admin’s actions would be:

  • ensure that it’s the same person
  • add temporary account (admin’s account) to the OD site owners as primary owner
  • remove the old Id from the OD site
  • add new user account to the OD site owners as primary owner
  • remove temporary account from the OD site

References