Tag Archives: Microsoft 365 Governance

KBA, how-to, thoughts related to Microsoft 365 SharePoint Governance

Orphaned Users in SharePoint and Their Connection to User ID Mismatch

When a user leaves an organization, their account is usually deleted from Microsoft Entra ID. However, SharePoint often keeps a record of that user in its own databases. These records are commonly called orphaned users. Most of the time they do not cause any problems. But when the same user principal name (UPN) is later assigned to a new account, these orphaned records can cause the well-known User ID Mismatch issue. In this article, we’ll look at what orphaned users are, why they exist, how they are related to User ID Mismatch, and what SharePoint administrators can do about them.

Overview

An orphaned user in SharePoint is generally understood as a user whose record still exists in a SharePoint, even though the corresponding Microsoft Entra ID account no longer exists in directory.

Orphaned user records are not necessarily errors. SharePoint maintains its own databases at every site and caches user’s data so that it can preserve historical context, such as who created or modified a document. However, these records can become operationally significant when an organization creates a new Entra ID account using the same User Principal Name (or UPN), as a previously deleted account.

This can produce a SharePoint user ID mismatch:

  • The old and new accounts have the same UPN, but different “internal” object IDs.
  • SharePoint keeps the old UPN and still associates the UPN with the old identity.
  • The newly created user receives permissions, but cannot access content (user id mismatch)

This article explains:

  1. What orphaned SharePoint users are.
  2. Why SharePoint retains them.
  3. How they contribute to user ID mismatch.
  4. Why fixing one affected site does not solve the tenant-wide problem.
  5. How remediation strategies differ by tenant size, tenant age, and employee turnover.
  6. How to approach the problem using cleanup, ticket prevention, and offboarding controls.

What Is an Orphaned User in SharePoint?

SharePoint maintains information about users who have interacted with or received permissions to a site collection. This information is stored in the site collection’s User Information List, commonly referred to as the UIL (it’s a hidden list in every SharePoint site collection). When a person visits a site or is otherwise resolved as a user, SharePoint caches information about that identity in this list. Deleting the corresponding account from Microsoft 365 or Entra ID does not necessarily remove the entry from each SharePoint UIL.

The resulting record is commonly called an “Orphaned user” or “Stale user” or “Legacy user” or “Orphaned SharePoint identity”. “Orphaned user” is a useful administrative term, although Microsoft documentation more frequently uses terms such as legacy user account, outdated user account, or an old entry in the UIL.

Why does SharePoint retain the user?

The retained record provides continuity for user-related metadata. For example, after an employee leaves the organization, other users may still need to see that the former employee:

  • Created a document.
  • Modified an item.
  • Added a list entry.
  • Was previously assigned permissions.
  • Participated in historical SharePoint activity.

From this perspective, the orphaned record appears not harmless but useful. It helps SharePoint preserve the historical identity associated with existing content.

Should administrators treat every orphaned user as something that must immediately be deleted? I see Microsoft position is conflicting/controversial/ambiguous, as generally they say that legacy entry in the UIL is needed to preserve metadata but – at the same time – removal an orphan user from the UIL is OK, though primarily as a troubleshooting action for profile synchronization and mismatched-ID scenarios, rather than as routine indiscriminate cleanup (more: Is It Safe to Remove a User from a SharePoint UIL).


The Problem Appears When an Identity Is Recreated

Consider a common employee lifecycle scenario.

  1. John Smith leaves the organization.
  2. His Entra ID account is deleted.
  3. SharePoint retains John’s entries in the UIL of sites where he previously appeared.
  4. A year later, the organization hires another John Smith
  5. The identity team creates a new Entra ID account using the same UPN, such as john.smith@contoso.com.

The new account looks similar to the old account: same display name, same email address, same UPN. However, it is not the same directory object. The recreated account receives a new internal identity value, even though its UPN matches the deleted account. Microsoft documents this as a primary cause of SharePoint and OneDrive user ID mismatch.

The same situation can also occur when the UPN is assigned to a rehired person.

From Entra ID’s perspective, the new account is a new security principal. From the affected SharePoint site’s perspective, however, the UPN may still be associated with the legacy UserInfo entry.


What Is a SharePoint User ID Mismatch?

A user ID mismatch occurs when the identity presented by the current user does not match the identity stored in SharePoint with the same UPN.

Conceptually, SharePoint sees something like this:

AttributeLegacy accountNew account
Display nameJohn SmithJohn Smith
UPNjohn.smith@contoso.comjohn.smith@contoso.com
Entra ID object IDUnique (Old value)Unique (New value)

Although the UPN is the same, the internal identity is different.

Microsoft describes the underlying cause as follows: the recreated account receives a new ID, but the affected SharePoint or OneDrive UIL still contains the old ID. When the user attempts to access the site using the new account, the new identity does not match the identity stored in the site. Access can therefore be denied.

Sometimes a user experiences issues with their personal OneDrive site (User Id Mismatch in OneDrive scenario).

Typical symptoms include:

  • An Access denied message, while permissions appear correct
  • A message stating that a legacy account with the same email exists

Why Denying Existing Access Is Correct

At first glance, it may appear that SharePoint should automatically connect the new account to the old account because the UPN is identical. But that would create a security risk.

The same UPN does not mean that the new account represents the same person. Even if it is the same person, the individual may have returned in a different position, in another department, under different security requirements. So the new account should not automatically inherit the old account’s SharePoint permissions.

Therefore, SharePoint is correct not to treat the recreated account as the same security principal merely because the UPN matches. The more problematic behavior appears after an authorized site owner intentionally grants the new account access.


Where the Actual Operational Problem Begins

Suppose the new John Smith requests access to a site.

The site owner reviews the request and intentionally approves it. Alternatively, the site owner shares a site, library, folder, or document with the new account. From the site owner’s perspective, everything may appear correct:

  • The expected name and email are displayed
  • The user appears in the proper group (or with proper direct permissions)
  • The sharing (or approval) operation completes without an obvious error

However, the user may still be unable to access the resource because the site’s UIL contains the legacy identity associated with the same UPN.

SharePoint does not replace the old identity automatically when the new account is granted access. That is the practical limitation behind the user ID mismatch incidents.

Microsoft’s supported starting point is the Site User Mismatch diagnostic in the Microsoft 365 admin center. When a mismatch is found, the diagnostic can offer to remove the old identity from the affected site. After the old entry is removed, the new account must be assigned the appropriate permissions.

For a single user and site, this is usually manageable. At tenant scale, it becomes much more complicated.


Why Fixing One Site Is Not Enough

A recreated user rarely interacted with only one SharePoint site. During the person’s previous employment, the account may have been present in:

  • Many Team sites – as user can contribute to many projects, be involved in different activities
  • Publishing (Communication sites) – as user access corporate intranet and other org-wide sites
  • Shared OneDrive sites, as by default all documents shared in teams chats are shared via Onedrive
  • Viva Engage connected sites, as there is a SharePoint site behind every community

Removing the legacy identity from one affected site fixes only that site. The same user may encounter another issue tomorrow, next week, or several months later when attempting to access a different site.

This creates a recurring support pattern:

  1. The user reports an access problem.
  2. The administrator identifies and fixes a mismatch issue at the reported affected affected site.
  3. The ticket is closed. User assumes his issue is fixed.
  4. The user encounters the same problem on another site.
  5. The investigation starts again. User is confused…

The technical fix is site-specific, while the identity lifecycle problem is potentially tenant-wide.


Why Discovering Every Affected Site Is Difficult

The obvious question is: Which SharePoint sites still contain the old identity?

SharePoint Online does not provide a simple out-of-the-box report listing every site collection whose UIL contains a specific legacy user. An administrator can technically scan SharePoint sites and inspect their users. However, this can be inefficient in a large tenant. For example, imagine a tenant with:

  • 50,000 SharePoint sites.
  • A user who appeared in approximately 100 of those sites.

A straightforward tenant scan may need to inspect all 50,000 sites to locate the relevant 100.

The administrator knows the identity being investigated but does not know which site collections contain that identity. SharePoint’s user information is distributed across site collections rather than exposed through a convenient centralized orphan-user inventory.

It is possible to use PowerShell, but even for one affected user, a tenant-wide brute-force scan may consume considerable time and service resources relative to the number of useful results. The other option is to use 3-rd party tools.


Shifting Left: When Should the Problem Be Addressed?

Can we be proactive here? Probably yes… There are three general opportunities.

Option 1: After a Ticket Is Reported for one site, fix all affected sites

This is a “reactive-proactive” approach… We get tickets (reactively) but fix not one, but all affected sites for a user (proactively)

Workflow

  1. A user reports that SharePoint access does not work.
  2. The administrator runs the Site User Mismatch diagnostic and confirms that the account was created with the re-used UPN and user experiences User Id Mismatch issue.
  3. The old user entry is removed from the reported site
  4. The administrator makes all efforts to identify all affected sites for the user, and fix these sites
  5. User is informed that the issue is fixed and that it must be a new share or approved access request

This approach is minimally proactive, it treats the symptom rather than the tenant-wide identity residue.


Option 2: Check Newly Created Accounts

The next shift-left opportunity occurs when an account is created. The idea is not to wait when user hits the issue. The organization could determine whether the UPN was previously used and then search for the corresponding legacy SharePoint identity, so the mismatch can be resolved before the user accesses SharePoint.

The challenge is the process must determine whether the UPN is genuinely new or reused. This approach can prevent tickets, but it requires reliable identity history.

Alternatively we can scan all new users to discover potential mismatched id, but this approach is much more expensive.


Option 3: Remove Legacy Site Entries During Offboarding

The earliest intervention point is employee offboarding.

Before deleting the Entra ID account, the organization still has a valid and identifiable user. It is easier to determine the SharePoint sites associated with a current identity than to reconstruct that information months or years later.

The offboarding process could be as follow:

  1. Disable user account
  2. Identify the SharePoint and OneDrive sites associated with the departing user
  3. Delete user account
  4. Remove the user from all sites UILs

Surely we know that most offboarded users will never return (deleted UPNs may never be reused) and removing every departing user from every site may be unnecessary, but it It addresses the problem at its earliest practical stage and ensures there is no future user ID mismatch incidents.

This is the most proactive approach, but it (as well as option 2) can also be an over-engineered solution if the actual mismatch rate is very low.

Again, as per Microsoft – an organization should not assume that universal deletion is automatically the best practice. Microsoft specifically describes UserInfo removal as a troubleshooting operation that should be performed for synchronization or mismatch scenarios when advised, rather than as a general cleanup requirement.


A Three-Workstream Strategy

For established tenants, a single activity not always completely solves the problem. A practical program can be a combination of three separate workstreams.

1. Clean Up Existing Orphaned Users

This workstream addresses the historical backlog already present in the tenant.

Imagine, we implemented remediation Option 3 (Remove Legacy Site Entries During Offboarding). For brand-new tenants that would guarantee no user id mismatch issues. But for mature tenants we already have a lot of legacy users, so we’ll definitely have issues related to mismatched is.

To ensure we do not have user id mismatch tickets – we wood need
– stop bleeding (implement Option 3 Remove Legacy Site Entries During Offboarding)
– clean-up existing orphaned users

Existing orphan users cleanup can require substantial effort in an old or large tenant because orphaned identities may have accumulated for many years, so we could have millions of orphaned users record (which means millions of deleting operations) – see more in “Estimate number of Orphaned Users and User Id Mismatch tickets.”

2. Stop Tickets

This workstream focuses on newly created or recreated accounts. Its purpose is to prevent a new employee or returning employee from encountering mismatch errors after receiving a Microsoft 365 account and before SharePoint access.

It does not remove the entire orphan-user backlog, so we’d still have a bunch of orphan users, but it can prevent visible incidents for newly created accounts. Having “Stop tickets” process implemented we guarantee user’s satisfaction, but that’s (imho) the most expensive process.

3. Stop the Bleeding

This workstream is triggered when users are offboarded. Its purpose is to prevent orphaned users, which would guarantee no new legacy identity conflicts. This is a future-state prevention activity.

Implementing “Stop Bleeding” process must be combined with clean-up efforts to achieve “Sop tickets”.
Imho, this is the most logical way to remediate the issue. It might be complicated from the engineering efforts perspective, but would be the less resource-consuming approach after clean-up.


Tenant Age aChanges the Priority

The appropriate combination of these workstreams depends partly on the age of the tenant.

New Tenant

A newly created tenant has little or no legacy identity history.

The primary focus should therefore be:

  • Offboarding design
  • “Brute force” clean-up efforts

Established (or Old) Tenant

An old established tenant with many years of account turnover already contain many unresolved legacy (orphan) users entries. We are probably dealing with existing (ongoing) user ID mismatch cases.

The organization may need all three workstreams:

  • Clean up existing records
  • Improve future offboarding
  • Dealing with (or preventing) current tickets

Tenant Size Determines the Technical Approach

Small Tenants

In a small tenant, brute-force scanning may be acceptable. An administrator may be able to:

  1. Enumerate all SharePoint sites.
  2. Enumerate the users on each site.
  3. Compare SharePoint identities with Entra ID identities.
  4. Produce an orphan-user report.
  5. Review and remediate the results.

A simple PowerShell script can be used (like this one from the “Orphan Users in Small Tenants” ). Depending on throttling, number of sites, the process might complete within a practical operational window.

Large Tenants

In a large tenant, a simple brute-force approach is impractical. This is not only “this should be done” but “this should be done in a most effective way” otherwise it might take forever. The solution may require:

  • Parallel processing with controlled concurrency
  • Throttling and retry handling
  • Delta-oriented identity processing
  • Site prioritization
  • Governance around retention and UPN reuse

At this scale, orphan-user management becomes an engineering and data-indexing problem rather than a simple administrative script. A 3-rd party tools might be required, in combination with custom PowerShell-based solutions.

Medium-Sized Tenants

To address an Orphaned Users and User Id Mismatch issue in a medium-sized tenant it may require a combination of approaches methods based on tenant size, age processes maturity, admins qualification and so on.


Employee Turnover Also Matters

Tenant size and age are not the only factors. Two organizations with the same number of users may experience very different levels of risk.

An organization with stable staffing and low turnover creates relatively few deleted identities. An organization that frequently hires contractors, seasonal workers, or temporary employees may create and delete a much larger number of accounts.


Is It Safe to Remove an Orphaned User?

This deserves its own detailed discussion.

Microsoft documents removal from the UIL as a way to troubleshoot mismatched identity and profile synchronization scenarios. At the same time, Microsoft warns that the removal procedure should be used for those troubleshooting purposes rather than as an unrestricted general cleanup method.

For additional analysis, see: Is It Safe to Remove a User from a SharePoint UIL


Another Way to Prevent User ID Mismatch: Identity Management

So far, we discussed the problem from a SharePoint administrator’s point of view. In that world, the typical solution is to find the legacy user in SharePoint and remove the old user entry from the User Information List.

However, there is another approach. Identity and Access Management (IAM) team can reduce or eliminate many User ID Mismatch issues by ensuring that each person receives a unique UPN that is never reused.

For example, instead of recreating:

john.smith@contoso.com

for a rehired employee, the organization could assign a different UPN, such as:

john_smith@contoso.com

or follow another naming standard that guarantees uniqueness.

With this approach, the new account never collides with the legacy SharePoint user record. As a result, User ID Mismatch issues do not occur.

Of course, this approach comes with its own challenges. Organizations often prefer to reuse the original UPN because it is easier for users, administrators, and business processes. In addition, changing naming standards may affect other systems that depend on predictable user names.

For that reason, UPN management should be viewed as an identity governance decision rather than a SharePoint administration task. SharePoint administrators can fix User ID Mismatch issues when they occur, but Identity and Access Management teams can often prevent those issues from appearing in the first place by implementing policies around account lifecycle management and UPN reuse.

In short, there are two ways to address User ID Mismatch:

  1. SharePoint approach: Find and remove the legacy SharePoint user records that cause the conflict.
  2. Identity management approach: Prevent UPN reuse so that the conflict never occurs.

The first approach is owned by SharePoint administrators. The second approach is owned by Identity and Access Management teams. In many organizations, the best long-term solution is a combination of both approaches.

Microsoft must address the issue

Anyway, the best possible resolution could be if Microsoft fix the product: at the moment when a new account is approved with access to the site (or site is shared by site owner with a user) – SharePoint can do clean-up internally – by replacing the old Id with the new Id.

References

Orphan Users in Small Tenants

“Orphan User” in SharePoint refers to a user account that no longer exists in Entra ID but is still present in the User Information List (UIL) on SharePoint sites.

Offboarded user accounts are usually deleted from the Entra ID directory sooner or later. However, SharePoint caches user information in its own databases. This information is stored in the so-called UIL (User Information List). Each site has its own User Information List.

Generally, orphan users are pretty harmless, as they are not users, but just ghost entities – records that reflects former accounts, i.e. these users cannot login, even when a new user is created with the same email – access is not possible. Moreover, legacy Microsoft documentation says such records are needed to preserve metadata – like who is the author of the document or documents editing history, etc.

So yes, orphan users are harmless until you hit a User ID Mismatch issue.

In a nutshell, a User ID Mismatch happens when an email address (UPN) is reused and a new user tries to access a SharePoint site where the old user previously had access.

SharePoint does not allow the new user to automatically inherit the same access that the old user had, and this is expected behavior. The issue is that SharePoint may fail to correctly grant access to the new user even after permissions have been assigned.

In such cases, you must first remove the old user ID from the site’s User Information List. This approach is recommended by Microsoft and considered as safe. And guess what? It turns out the old user is no longer needed in the UIL to preserve metadata 🙂

When a user hits a User ID Mismatch issue, it is often difficult to recognize that the problem is not simply missing permissions or a site owner not approving access, but an actual product limitation that prevents access to SharePoint. As a result, users become frustrated, support teams spend time troubleshooting the issue, and it may take a while before the root cause is identified and resolved.

So why not remediate the issue proactively? This way, there are no high-priority support tickets, no angry users, and no urgent troubleshooting when the problem eventually occurs.

The engineering problem behind all approaches to proactively resolving the User ID Mismatch issue is that there is no out-of-the-box (native) SharePoint report that provides a list of sites where a specific orphan user is present. You cannot simply press a button and get a complete list of orphan user/site pairs.

In general, you need to scan the entire tenant, site by site, including personal OneDrive sites, and retrieve all historical site users. Then you need to check whether each user stored in SharePoint still exists in Entra ID.

Multiply the number of sites by the number of users and see how long it might take. An average user typically has access to only ~1% of all sites in a tenant, so you can imagine how inefficient this approach can be.

However, for small tenants, we can still use this so-called brute-force approach. With this approach, we use PowerShell to do the job: identify all orphan users and, optionally, remove them.

Whether this is a viable solution depends on your specific situation: the size of your organization, employee turnover, the amount of data (number of sites), and the age of the tenant.

I may provide some kind of calculator in the future to estimate how long the process might take based on tenant characteristics. But the general idea is simple: in some cases, a brute-force approach is perfectly acceptable because it:

a) is very simple and does not require advanced PowerShell skills, and
b) can be completed in a reasonable amount of time (minutes or hours)

The scripts are here: https://github.com/VladilenK/m365-User-Id-Mismatch

References:

Content Security Policy (CSP) in SharePoint Online

Microsoft enforces Content Security Policy (CSP) in SharePoint Online.
What does that mean to SharePoint Admins? Should we be concerned? What do we need to undertake? Before? After?

Generally, in web development – the policy (Content Security Policy – CSP) is needed to minimize the risk of security threats by controlling which resources, in particular JavaScript resources, a page/site is allowed to load.

In SharePoint web development is done via SPFx, so the CSP policy affect SPFx solutions. In a nutshell, from now on, for the SPFx solutions to work properly, admins should whitelist external domains. Admins can maintain allowed domains list via GUI in SharePoint admin center or via PowerShell:

# List current sources
Get-SPOContentSecurityPolicy
# Remove a source
Remove-SPOContentSecurityPolicy -Source "https://cdn.host.com/source/"
# Add a source
Add-SPOContentSecurityPolicy -Source "https://cdn.host.com/source/"

The CSP policy was enforced on March 1, 2026, but as per Microsoft, if clients need more time to review and update existing SPFx solutions, we can delay the enforcement by 90 days, until June 1, 2026, via

Set-SPOTenant -DelayContentSecurityPolicyEnforcement $true
# IMPORTANT: List the applied setting again as mandatory step to correctly persist the setting (will be fixed)
(Get-SPOTenant).DelayContentSecurityPolicyEnforcement

Admins can view the Content Security Policy Violations via Purview.

So there are cmdlets:

  • Add-SPOContentSecurityPolicy
  • Remove-SPOContentSecurityPolicy
  • Set-SPOTenant

And for the Set-SPOTenant cmdlet there are options related to CSP:

  • DelayContentSecurityPolicyEnforcement
  • EnforceContentSecurityPolicyConfiguration
  • ResyncContentSecurityPolicyConfigurationEntries
  • ContentSecurityPolicyEnforcement

So the question I ask for myself is what exactly each command does and how are the options correlated to each other and affect SPFx solutions.

Content Security Policy (CSP) in SharePoint: My Findings

ContentSecurityPolicyEnforcement

It seems like using Set-SPOTenant with a ContentSecurityPolicyEnforcement parameter change nothing. I.e. “Set-SPOTenant -ContentSecurityPolicyEnforcement:$false” does not disable policy and vise versa
“Set-SPOTenant -ContentSecurityPolicyEnforcement:$true” does not enforce the CSP policy.

My guess it’s because this article is written in April 2026. Microsoft started Content Security Policy (CSP) enforcement since March 1, 2026. So probably before March 1, 2026 we could use ContentSecurityPolicyEnforcement to enable the policy, but since March 2026 the policy is enforced anyway and parameter ContentSecurityPolicyEnforcement is not needed (and probably will go away in the next versions of the Microsoft.Online.SharePoint.PowerShell Module).

DelayContentSecurityPolicyEnforcement

DelayContentSecurityPolicyEnforcement parameter effectively switches the policy on and off. It takes a few minutes for Microsoft to propagate the change across so you can start seeing the policy enforced or not. But this is true only during 90 days – in Mar, Apr and May 2026. Since June 1, 2026 the Content Security Policy (CSP) will be enforced in SharePoint Online.

Testing SPFx Solutions Before Enforcement

How do I know if my site compliant with CSP or not before CSP enforcement?

There are some good findings for developers in the article Preparing for SharePoint Online CSP Enforcement by Nello D’Andrea, MVP. But I will share some more.

Use browser’s dev tools (F12). Select console and filter/search output with “policy”. You can find something like:

“Loading the image ‘<URL>’ violates the following Content Security Policy directive” or
“Loading the script … violates the following Content Security Policy directive” or
“Executing inline script violates the following Content Security Policy directive” or

If the message is just informational (in white) and there is also “The policy is report-only, so the violation has been logged but no further action has been taken.” that means the policy is not enforced yet… and the site functionality should not be affected.

Otherwise – when you see the same “… violates the following Content Security Policy directive” in red – this would be an error message and the policy prevents something on your site due to the CSP policy so functionality will be broken.

References

Orphaned Users Clean-Up in large Microsoft 365

This article address “Orphaned Users” in SharePoint and applies mostly to medium and large tenants.

The problem statement

Orphaned users are user accounts that no longer exist in Entra ID (Azure AD) but still appear inside Microsoft 365 SharePoint or OneDrive sites, specifically in the User Information List (UIL). A SharePoint User Information List (UIL) is a hidden system list that exists in every SharePoint site collection and stores cached profile information about users who have interacted with that site. In short about orphaned users and UIL: The identity is gone, but its footprint remains.

Why Orphaned Users Must Be Removed?

Orphaned users should be eliminated not only because their presence in sites confuses active users, but mostly because they cause “User ID Mismatch” issues when UPNs are reused.

What is a “User ID Mismatch” issue in SharePoint?

User ID Mismatch is a known problem in SharePoint. It happens usually when a user account is deleted from the directory, and then a new account is created with the same UPN (re-used user principal name). Symptoms are: a user is provided with the access to the site, but still cannot get access.

The reason behind it is that SharePoint caches users data in the UIL, including not only UPN, but also Entra Id user object Id. So when a re-used UPN tries to access the site – SharePoint does not allow access, because even if UPN is the same – Id is different – e.g. SharePoint treats user as a different one. So access needs to be re-provided. And this is where the actual issue happens. When a site owner shares the resource with a new user (or approves access request) – Microsoft does dot update the UIL with the new user ids. So for the user and for the site owner it looks like access was provided, but in fact it was not.

How do we remove Orphaned Users

Microsoft provides a “fix”, but this solution is really weak as it allows only to remove one orphaned user from one site reactively. Here are some more details: “Fixing SharePoint User ID Mismatch Issue“.

Can we address the issue proactively, tenant-wide (all users, all sites, before the issue happens)? Probably – yes, but it takes a lot. Here are some more details: “Preventing SharePoint User ID Mismatch: a Tenant‑Wide Approach“. In a nutshell solution is at the moment of an employee offboarding – when a user account is deleted from directory (Entra Id) – we need to remove that user from all sites UIL they had access to. But how? And the other question: is it safe?

How do we remove deleted Entra is users from all SharePoint sites? This is a huge problem, as there is no native (out-of-the-box) Microsoft’s tools or reports to get all sites a specific user has access to. But here is where a 3-rd party tools might help. E.g. SysKit Point – with it’s “Orphaned Users” policy or ShareGate.

Is it safe to remove all orphaned users from all sites in SharePoint? Though Microsoft did not publicly say “yes” (at least I have not seen it), a high-skilled SharePoint support engineers says yes, generally it’s safe if you do it correctly. My research on the question says the same – yes, it is safe (“Is It Safe to Remove a User from a SharePoint UIL?“).

Can we just turn the SysKit’s “Orphaned Users” policy on? In small tenants – yes, in new tenants – yes. But your tenant is not new and not small – you probably already have tens or hundreds of thousands of orphaned users. Unfortunately, in SysKit there is no options to implement the policy in chunks – so we do orphaned users clean-up against test sites, then pilot, then step-by-step all other sites. Also the “orphaned users” report just fails due to enormous amount of data.

So the idea is to do an initial clean-up in the environment – gracefully remove all existing orphaned users before implementing “Orphaned Users” policy. This is exactly the topic of this KBA.

Initial Clean-Up of Orphaned Users in large Microsoft 365 tenants

A controlled, script-based clean-up must be completed before the Orphaned Users policy can be safely enabled. PowerShell is identified as the primary tool for this effort.

Below is a draft (preliminary considerations) – to be tested/proved/updated.

Scale of the Problem (sample large Microsoft 365 tenant):

  • Approximately 500,000 sites (~200k SharePoint + 300k OneDrive sites)
  • Approximately 500,000 orphaned users
  • Approximately 300,000 normal users

Key Constraints and Challenges

  • No existing report that maps orphaned users to sites
  • Full enumeration of sites and users is expensive and time-consuming
  • Microsoft throttling limits must be respected
  • Some sites have extremely large User Information Lists (UILs)
  • Orphan detection must not rely on UPNs due to reuse
  • Processing must be resumable and trackable

High-Level Strategy

The clean-up approach must:

  • Support piloting and phased execution
  • Reduce orphaned user count enough for SysKit reporting to function (no need in total “zero orphan” cleanup)
  • Minimize tenant-wide risk

Recommended initial strategy:

  • Exclude new sites and external sites
  • Identify large sites and process them separately
  • Begin with medium-sized sites
  • Validate approach using small but active sites before scaling

Execution Model

For each site processed:

  • Retrieve users from the site’s User Information List (UIL)
  • Check each user to determine orphan status
  • Remove orphaned users immediately
  • Avoid report-only runs except for limited analysis

Deleting orphans immediately avoids duplicate scanning and unnecessary re-validation.

Orphan Detection Approach

Preferred identifier: Entra ID Object ID. UPNs must not be used to determine orphan status due to reuse.

Options considered:

  1. Query Entra ID for every user
    • Accurate but expensive
    • Repeats checks for the same users
  2. Maintain a cached list of existing users
    • Risk of missing newly added users
    • Large list reduces efficiency

Recommended technique:

  • Maintain a list of orphaned users by Entra Object ID
  • If Object ID is known orphaned, it is orphaned everywhere permanently
  • Check UIL user Object ID against this list first
  • If unavailable, fall back to Entra ID lookup

Note: UIL does not always store Entra Object ID directly; sometimes only login name (claim) is available.

Handling Large Sites

  • Get-PnPUser does not support paging
  • Direct access to the User Information List (UIL) with paging is required
  • Large UILs can cause failures if not paged properly

Workers and Parallel Processing

The clean-up cannot be completed with a single script run.

Expected characteristics:

  • Hundreds or thousands of executions
  • Parallel workers required
  • Throttling must be handled gracefully
  • Processing must be resumable

Worker execution options:

  • Manual runs from a VM (e.g., nightly)
  • Scheduled Azure jobs (Function App or Automation Account)

With multiple workers, a global STOP flag should be supported.

Tracking and State Management

Tracking is mandatory to avoid reprocessing completed work.

Tracking by user-site pairs is not feasible due to scale.

Preferred approach: Tracking by site.

Minimum tracking fields per site:

  • SiteUrl
  • State (Pending | InProgress | Done | Failed)
  • LastProcessedDateTime
  • AttemptCount
  • LastError
  • Metrics:
    • UsersScanned
    • OrphansFound
    • OrphansRemoved
    • DurationSeconds

Tracking Storage Options

  • SharePoint list: not suitable at scale
  • CSV:
    Pros: simple
    Cons: slow, co-authoring issues
  • SQL:
    Pros: fast, reliable
    Cons: complex
  • Azure Table Storage or Cosmos Table API: viable option

Each worker:

  1. Takes a site
  2. Marks the site InProgress (with a lease)
  3. Scans UIL in pages
  4. Removes orphaned users
  5. Logs actions and metrics
  6. Marks site Done

Reused UPNs and User ID Mismatch

Because the tenant contains many reused UPNs:

  • UPN must not be used to determine orphan status
  • Entra ID Object ID must be used wherever possible

Deleting users by site user ID or login name is safe because reused UPNs are not added to UIL until the previous orphan entry is removed.

An alternative approach is to skip reused UPNs entirely:

  • This is safe from a risk perspective
  • But it misses an opportunity to fix User ID Mismatch issues

This tradeoff may be acceptable if performance gains are significant.

References

Is It Safe to Remove a User from a SharePoint UIL?

Actually, this article is more about “Is it safe to remove all deleted user accounts from all SharePoint sites UIL?”, as managing user lifecycle changes in Microsoft 365 goes far beyond deciding whether it’s safe to remove a single user from an individual SharePoint UIL. In large Microsoft 365 tenants, deleted or inactive accounts – sometimes called orphaned identities – can create clutter and confusion in permissions and UI elements affecting governance clarity, audit readiness. This KBA explains the broader tenant‑scale implications of cleaning up deleted user accounts across all SharePoint sites.

My immediate motivation was researching the ‘User ID Mismatch’ issue in SharePoint and figuring out how to address it proactively across the tenant. Why a dedicated KBA? Because, In isolated cases, it’s generally considered safe to remove a single user from a single SharePoint UI location after their Entra ID account has been disabled or deleted. However, there is no official guidance recommending a tenant‑wide cleanup of all UI entries for disabled or deleted accounts. In fact, when asked why such cleanup might be needed, Copilot typically responds that performing it tenant‑wide is not considered safe.

One of the reasons Copilot says it is not safe is

“Avoid removing UIL entries if you need historical metadata
For example, if you rely on “Created by” or “Modified by” or Version history tracking

In my personal experience, removing a user from the UIL does not affect item edit history — the removed user still appears correctly. Moreover, when a new user with the same UPN/email but a different display name is added to a site and begins working on the same document, SharePoint handles this correctly. But let’s test it to confirm or refute this.

I have created 3 new accounts in tenant and provided them with an m365 license:

Then created a test site, and all three users one-by-one were working on the site, creating documents, lists, providing permissions

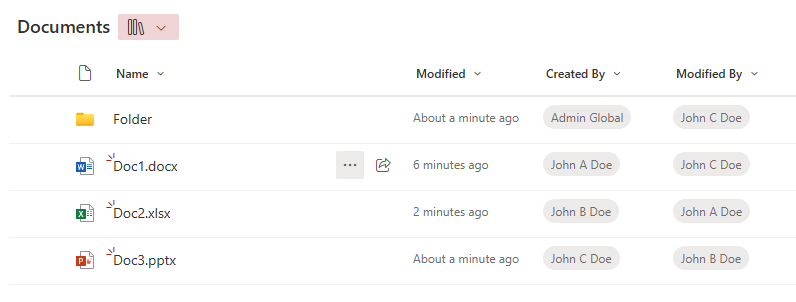
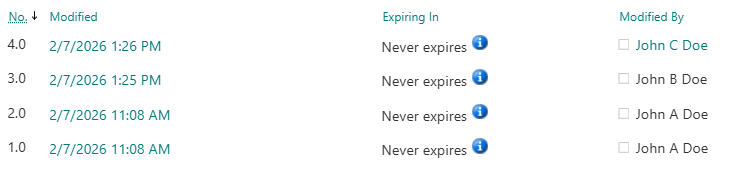
Ensure that “Created by” or “Modified by” and Version history are tracking users correctly:

Now let us delicense, disable and delete all three users – John A Doe, John B Doe and John C Doe.
These does not change anything, as users are still in the UIL. Now let me remove all three users from the site UIL. Sources say that “Microsoft has a series jobs to clean-up users after deletion” and “never re-create users within days after deletion, wait at least 30 days.”

So let me check what is happening with “Created by”, “Modified by” and “Version history” after we delete users from the UIL and re-create users with the same UPN and provide access to the site…

EventConsequenses
User deleted from Entra Id and from UILall looks good
After a few minutesall looks good
After a few hoursall looks good
User John A Dow is recreated with the same UPN
(less than 24 hours since deletion), provided with permissions to the site and started working on documents
all looks good
After a few minutesall looks good
After a few hoursall looks good
User John B Dow is recreated with the same UPN
(less than 7 days since deletion), provided with permissions to the site and started working on documents
all looks good
After a few minutes, and after a few hoursall looks good
User John C Dow is recreated with the same UPN
(less than 30 days since deletion), provided with permissions to the site and started working on documents
TBP
After a few minutes, and after a few hoursTBP

So far all looks good, i.e. I’m not seeing any issues.

Proof is below (in the form of screenshots):

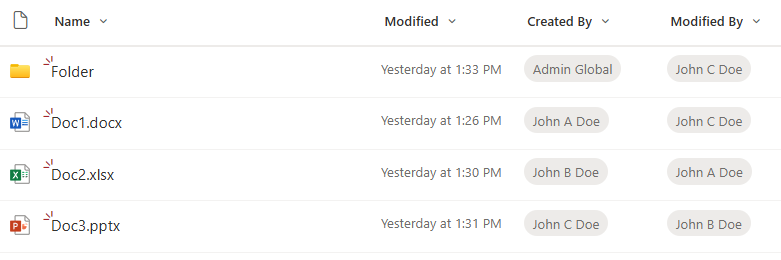
Users deleted from Entra Id and from UIL, after a few minutes:

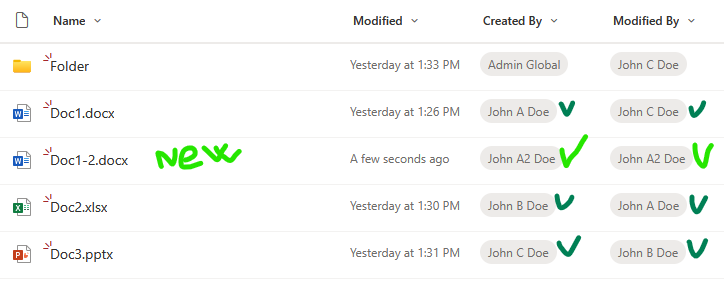
After ~1-2 hours, I created a user with the same UPN “John.A.Doe@vladev.xyz” but with different display name – “John A2 Doe”. A new user requested access to the site, got approval and was able to access the site with no issues, then created a new document. Here is how it looks like:

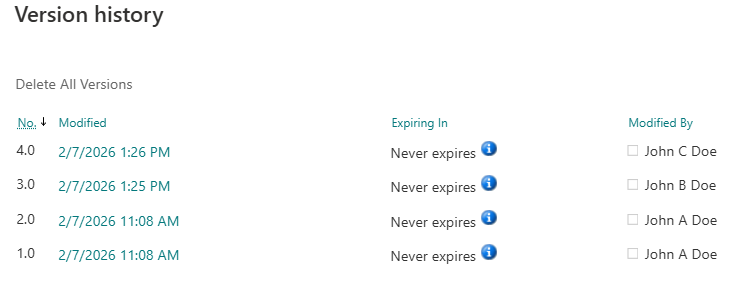
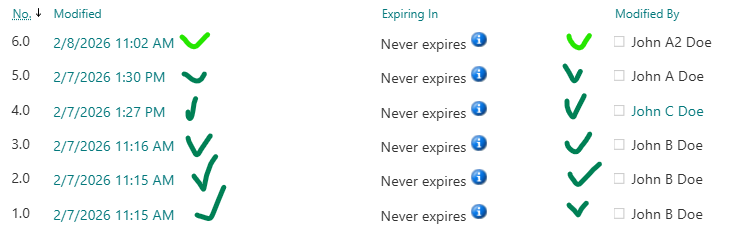
Then a new user – John A2 Doe – updated Doc2. Again, all looks good. An old John.A.Doe and a new John.A.Doe are reflected correctly. Here is the version history:

Let us wait for 24+ hours…

After 10 days I undeleted “John B Dow”. Checked their access to site – permissions are here. Why? It turns out I did not remove the user from the associated Microsoft 365 group. So when I restored (undeleted) account from Entra Id – the account regain groups membership. And after some time the user was able to access the site correctly. I did not expect that, and I’m not sure is it OK. I need to keep this in mind.

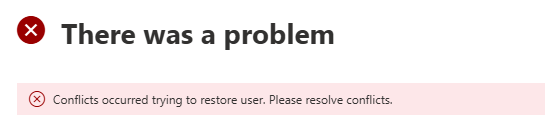
Now let me try to undelete “John A Dow” (remember I already created another account with the same UPN). User accounts that you can find under “Deleted Users” have a username like “457be210d0344040a530dc99cfaa2ba6John.A.Doe@contoso.com”.
Admin center did not let me undelete this account. The message I got was “There was a problem” and “Conflicts occurred trying to restore user. Please resolve conflicts.”. So that is OK as well.

User Information List (UIL)

In short, User Information List (aka UIL) is a hidden system list that exists in every SharePoint site collection and stores cached profile information about users who have interacted with that site.

The UIL is normally hidden, but you can access it adding the following to the site URL: “/_catalogs/users/simple.aspx”, “/_catalogs/users/detail.aspx” or “/_layouts/15/people.aspx?MembershipGroupId=0”, e.g.

https://<site-collection-url>/_catalogs/users/simple.aspx
https://<site-collection-url>/_catalogs/users/detail.aspx
https://<site-collection-url>/_layouts/15/people.aspx?MembershipGroupId=0

References

Preventing SharePoint User ID Mismatch: a Tenant‑Wide Approach

There is a known problem in Microsoft 365 SharePoint called “User ID Mismatch”. It happens if a user account is deleted from the Entra Id directory, and then a new account is created with the same UPN (e.g. rehired person or a person with a popular name like John Smith). Symptoms are: a user is provided with the access to the resource, but still cannot open it and gets “Access denied” error or “Sorry, something went wrong” and “There is a legacy user account in this site with same email. Please ask site owner or administrator to remove the legacy user account from this site”.

The reason behind it is that SharePoint stores users data in it’s own database (accessible via hidden system list called User Information List – UIL). Properties include display name, title, UPN, and (!) AD SID and Entra Id user object id. So when a re-used UPN tries to access the SharePoint site – Microsoft 365 compares Ids and declines access. So access needs to be re-provided. And this is where the actual issue appears.

If the site was accessed by the “old” user in the past, site UIL contains information about that “old” user. When the site owner shares the site with the “new” user – Microsoft does dot update the UIL with the new user ids. Microsoft 365 behave “normally”, no error messages are displayed. So for the user and for the site owner it looks like access was provided, but in fact it’s not.

Existing fix

Microsoft knows about the issue. But instead of fixing the root cause – Microsoft recommends removing the old user from the UIL. Obviously this fix is a) reactive, b) for one specific user and c) for one specific site. In my previous article – Fixing SharePoint User ID Mismatch Issue – I explained the issue in details, outlined 3 options to fix the issue, including PowerShell script.

Again, the issue is scoped with a specific site (site collection). The mentioned PowerShell-based solution and all Microsoft’s fixes are designed for one specific site, but in real life what is happening is the “old id user” had access to many sites, and “new id user” has access to many sites, so after a several “access denied” issues a user might be confused and ask SharePoint admins to fix the issue “everywhere”. We should not bother users with “please provide us list of site Url you are having issues with”… or saying to user “please create a new ticket when you hit the same issue again” also does not sound nice.

The issue is tricky to recognize. From the user perspective it looks like “normal” permissions issue – so it takes some time for user and site admin to realize that something is wrong and reach support. So can we do it proactively? I mean, can we prevent the issue to appear instead of fixing the issue after a user hit the issue?

Let us try to go deeper into the issue, as we would need to start from basics to find some more consistent solutions. Again, approaches could be

  • Simple Reactive: once we got an “Access Denied” ticket – we check if it is a user id mismatch and fix the issue for a site we got ticket for
  • Reactive – Proactive: once we got an “Access Denied” ticket – we check if it’ i’s a user id mismatch and not only fix the issue for a site we got ticket for, but also try to find all sites with the user id mismatch issue for the same user
  • Proactive – we’d fix the issue before the user hit Access Denied error due to User Id Mismatch issue. Options are
    • once a new user created in Entra Id – check if it’s a reuse upn case and if so – act accordingly – try to find all sites previous user had access to and remove old id from these sites
    • once a user deleted from Entra Id – get all sites user had access to and remove the user from accessed sites

Reactive – Proactive: Fix all sites for one specific user

We know how to fix the issue for one user at one site (here). But the User ID Mismatch issue does not come for a one site and one user. Usually it impacts many sites.So how do we fix the User Id Mismatch Issue on all sites for a specific user?

At first, the solution looks simple: we need to check all sites old user had access to and remove UPN from UIL. Well… yes… But how do we get a list of sites the old user present in the UIL?

Spoiler alert: So far – I’m not seeing a good solution. But let us go through possible options.

Option 1: Brute force – scan all sites

  • Get list of all tenant sites
  • For every site – try to get a user from the UIL
  • If present – check if this is a User Id Mismatch case
  • If yes – remove the user from UIL

This option is comprehensive, i.e. it should fix the issue for all sites, so in case of reused UPN we should not have issues for any tenant site for the same user. But this is a really “heavy” solution and can work well for small tenants only. I do not think this option is feasible for medium or large tenants.

Option 2: Access report.

There are 3-rd party tools (I’m not aware if there is a built-in m365 tool for that) you can use to get report on all SharePoint resources user have access in tenant. So you’d export the list, select unique sites Urls and scan these sites. Possible issues – usually we no not know how the 3-rd party tool builds this report (if the UPN or object Id is used), would it be “old” user access report or “new” user access report?

Option 3: membership

We can use MS Graph “membership” and “people” API to get list of sites around. We can get our user membership – m365 groups and related sites. People API would return users related to our client – a collection of person objects based on their relevance to the user, which is determined by the user’s communication and collaboration patterns, and business relationships. We can get these people OD sites, we can get their groups memberships and sites. We can do the same for people related to people. NB: I know, this option would give us sites related to a new user, not old user.

Add-on to Option 3: common sites.
With Option 3 we’d get group-based and OD sites. How about standalone sites? Also there might be public teams…
Usually in any tenant number of group-based sites (teams sites) are much bigger than non-group-based sites. So we can simply scan all standalone sites. But, again, in large tenants this might not be a feasible option. But we can get list of “open” standalone sites and public teams and Yammer communities (i.e. “common sites” usually accessed by everyone in tenant). Additionally, over the time we can get “most popular impacted sites” form the fixing history to update our list of common sites.

Option 5: audit log

Reactively, we can use audit log to get AccessDenied sites for a new user

  • Get audit log and filter it by user and select only “AccessDenied” pages
  • Make a unique list of accessed sites
  • For every site – check if this is a User Id Mismatch case
  • If yes – remove the user id from site’s UIL

What I do not like here is getting audit log is a slow operation, and still re-active. I use it when I cannot reach impacted user and I need to know list of sites user already having issues with.

Practice

My personal experience.
Option 1. In my simple tests – it takes ~1 hour to scan ~500 sites (keep in mind, we need to scan all sites, including personals/OneDrive).
Options 2 and 3 helps, as allows to cover majority of impacted sites our re-used UPN user might have issues with. But we cannot guarantee we fixed all sites for the specific user.

Fix all sites for all users proactively

The older your tenant is – the more reused UPNs you get. The bigger the tenant – the bigger the problem.

Obviously, for proactive solution, we need to start from Identity Management. Below are just thoughts so far…

No re-used UPNs.
Providing a unique UPN each time we create a user might help.

Know re-used UPN.
If we knew every reused UPN at the moment of account creation (an employee onboarding) – we could proactively apply Options 1,2,3 from our reactive approach.

Total clean-up
In theory – we could use our reactive Options 1, 2, 3 and 5 at the moment of the employee off-boarding to find all sites user had access to and just remove the terminated employee’s account from all sites UIL.
That would prevent user mismatch Id in the future. Removing a user from UIL should not impact edit history – i.e. user’s Name will still be populated correctly if you want to check versions history of documents created or updated by this user. Scanning all sites for every off-boarded employee could be an option for small tenants.

3-rd party tools

There are 3-rd party tools (e.g. SysKit Point).

SysKit’s Orphaned users governance policy currently is very simple, but new updates – i.e. Dec 16, 2025 – as advertised would allow to reove orphaned users automatically from sites. Once I got this update installed – I’ll test it and share here, as if all good – this might be the only real solution to a user id mismatch issue.

Hybrid Approach: PowerShell + SysKit Point

One of the approaches could be:

  • select a few sites everyone in the org should be accessed at least once (onboarding site, root site, corporate portal etc.).
    Get all users from the UIL and check against Entra Id if the user is present – this would give us a list of Orphan Users (more or less… a good approximation)
    Alternatively – for small tenant – SysKit has an “Orphan Users” report
    This needs to be done, e.g. monthly
  • build an automation – job that runs e.g. daily The job:
    get users delta from Entra Id, select new users, check every new user against orphan users list, create alert – “we got a reused upn, please act proactively to resolve a potential user id mismatch issue”
  • use SysKit to get report on orphan user sites
  • remove the old user from sites

this approach allows us work proactively and prevent user id mismatch issue, it can be semi-automated as it still require some manual steps – e.g. get sites accessed by an orphan user report from SysKit

The other approach would be as follow:

  • build a scheduled job that gets delta from an Entra Id, run it e.g. daily
    select deleted users
  • use SysKit API to get report on user’s permissions
  • remove user Id from sites

this approach would eventually fully resolve the issue and can be fully automated

Bottom Line

Currently, there is no out-of-the box or free, effective, tenant-wide, proactive solution that guarantees protection from user id mismatch issue. The bottleneck here is inability to quickly get list of sites a user had access to (we’d need 3-rd party tools for that).

Custom PowerShell scripts would work only in small environment, as the “total scan” approach would hardly be realistic in large environments.

There are though 3-rd party tools that build it’s own database with all the permissions of all users, which could be the foundation for the “Prevent user id Mismatch” functionality. Some tools even have the issue addressed (e.g. SysKit Point has an orphan users policy).

References

Proactive SharePoint: Essential Initial Configurations for Every New Microsoft 365 Tenant

In this article I will share what I would recommend to configure on every new Microsoft 365 Tenant.

The Challenge: Why Many Microsoft 365 Tenants Become Unmanageable and Inefficient Over Time

Many organizations adopting Microsoft 365 quickly discover that while the platform offers immense power, its default configuration often leaves crucial features disabled. These “dormant” functionalities, designed to enhance data governance, search capabilities, content management, and user experience, remain untapped. The real problem arises when a tenant matures: as users populate SharePoint sites and OneDrive accounts with vast amounts of information, and as collaboration intensifies, attempts to enable these critical features become incredibly complex, disruptive, and even risky. Retrofitting governance, re-indexing content, or restructuring information architecture on an existing, data-rich tenant can lead to compliance headaches, data inconsistencies, user frustration, and significant administrative overhead. SharePoint administrators frequently struggle with the technical debt accrued from these missed initial configurations, spending countless hours trying to bring order to an environment that could have been optimally set up from day one.

Consider the following.

Ownerless resources

Having an owner for every Microsoft 365 resource should be enforced from day one.

Sensitivity labels

This step is an essential prerequisite for the other governance features. I have an article explaining ownerless Microsoft 365 groups policy in details and more KBAs regarding ownerless SharePoint resources.

Oversharing in SharePoint

Oversharing in SharePoint is a serious problem. The earlier you start addressing it – the easier you life as SharePoint engineer. Here are some thought: Control Oversharing in SharePoint Online: Smarter Access Management in Microsoft 365

User profiles to Term Store mapping

There is an OotB misconfiguration in Microsoft 365 User Profiles mapping to Term Store Metadata. Here is the KBA how to configure User Profiles correctly.


WIP


Why this approach?

  • Relatability: It immediately speaks to the pain points experienced by many SharePoint admins (“unmanageable,” “inefficient,” “struggling with it,” “technical debt”).
  • Highlights the “Why”: It explains why these features are off and why it’s a problem to turn them on later.
  • Emphasizes Proactivity: It sets the stage for your solution, which is about proactive setup.
  • Strong Call to Action (Implied): It makes the reader understand that your KBA will provide the solution to avoid these common pitfalls.

Controlling Oversharing in SharePoint Online: Smarter Access Management in Microsoft 365

Oversharing remains one of the most persistent challenges in SharePoint Online. With the introduction of Microsoft Copilot and its AI-powered search capabilities, the issue has become even more visible—and more urgent to address. Microsoft has acknowledged this by introducing the SharePoint Advanced Management suite, aimed at helping administrators to bolster content governance throughout the Microsoft Copilot deployment journey.

Why Does Oversharing Happen?

In most cases, oversharing is unintentional. Based on my experience, the root causes typically fall into four categories:

  1. Unaware Sharing: A user shares a site, library, or folder without realizing it contains sensitive information.
  2. Unaware Uploading: A user uploads sensitive content to a location that is already broadly shared.
  3. Human Error: Mistakes like selecting the wrong group or sharing a folder instead of a file.
  4. Convenience: Users opting to share with “Everyone” to avoid the hassle of managing individual permissions.

Why It’s a Bigger Problem Today

In the past, search in Microsoft 365 was content-driven—you had to know what you were looking for. Today, search is context-driven. Microsoft 365 proactively surfaces content with suggestions like “Here’s what might be interesting to you” or “Here’s what others are working on.” This increases the risk of oversharing content being exposed.

Separate issue, non-technical, but related to the subject – not every user knows that search in Microsoft 365 is security-trimmed, i.e. provides results from only what this specific user has access to. Sometimes people might think of Microsoft 365 search the same way as general internet search (If a can see it – then everyone can see it, or why my private documents appear under Bing search?).

The Admin Dilemma

As SharePoint administrators, we’re caught in a classic catch-22:

  • Complex Microsoft products
  • Users prone to mistakes
  • Management demanding simple, fast solutions

What seemed like straightforward fixes for oversharing actually concealed the true issue, generating new problems, increasing admin burden, perplexing users, and ultimately hurting company productivity. Examples are (I would never do that):

  • Exclude sites from search indexing (Set “Allow this site to appear in search results?” to No)
  • Turn off Item insights, turn off People insights (turn off Delve)
  • Truncate enterprise search with “official” sites only (via query)

Microsoft offers two solutions: “Restrict discovery of SharePoint sites and content” and “Restricted SharePoint search”. Both solutions aimed to exclude content from search and from Copilot. Microsoft: “Restricted SharePoint Search allows you to restrict both organization-wide search and Copilot experiences to a curated set of SharePoint sites of your choice… and content users own or that they have previously accessed in Copilot.”. “With Restricted Content Discovery, organizations can limit the ability of end users to search for files from specific SharePoint sites.”

Microsoft clearly says that “limit the ability of end users to search” is a temporary measure that “gives you time to review and audit site permissions”… “to help you maintain momentum with your Copilot deployment while you’re implementing comprehensive data security”. Also: “Sites identified with the highest risk of oversharing can use Restricted Content Discovery to protect content while taking time to ensure that permissions are accurate and well-managed”.

Microsoft highlights that “Overuse of Restricted Content Discovery can negatively affect performance across search, SharePoint, and Copilot. Removing sites or files from tenant-wide discovery means that there’s less content for search and Copilot to ground on, leading to inaccurate or incomplete results”.

And finally “Restricted Content Discovery doesn’t affect existing permissions on sites. Users with access can still open files on sites with Restricted Content Discovery toggled on.”. I.e. solutions “Restricted SharePoint Search” and “Restricted Content Discovery” do not solve the root cause of the problem (oversharing), but make the problem less visible.

With over 15 years of experience in SharePoint and more than a decade working with Microsoft 365 and Azure—including large-scale tenants—I’ve seen this problem evolve. Now, with Copilot in the mix, it’s more critical than ever to implement a robust access management strategy.

Controlling Oversharing in SharePoint Online: Smarter Access Management in Microsoft 365

How to solve the real oversharing problem
(My Ideal “No-Oversharing” Tenant Configuration)

Here’s what I would recommend for minimizing oversharing in a Microsoft 365 environment (think of it as SharePoint Governance):

1. Remove “Everyone” and “Everyone Except External Users”

Disable these groups in the people picker to prevent broad, indiscriminate sharing. Instead, provide other options for sharing content with larger audiences (see below).

2. Implement Sensitivity Labels for Sites

  • Enforce mandatory sensitivity labels for all sites.
  • Labels should control site visibility (e.g., Private, Public) and be clearly named

The label is visible across all interfaces—Teams, SharePoint, libraries, lists, folders—so users always know how wide the content is shared from the sensitivity label.

3. Empower Users with Guardrails

  • Allow users to create Teams and communities, but enforce sensitivity labels.
  • Enable requests for standalone sites (Team or Communication) with required labels.
  • Disallow private or shared channels under public Teams to avoid label mismatches (e.g., a private channel labeled “Public”).

Benefits of This Approach

Once implemented:

  • Users will always know whether a site is private or public.
  • Sharing with “Everyone” on private sites will be technically impossible.
  • Users needing broad access can request public sites, e.g.
    • Public Teams for collaboration with everyone (allows read/write access)
    • Communication site for publishing information (allows read only access)

Yes, this may lead to more sites and Teams. Yes, this may lead to more tickets from users who at private site wanted to break permissions as usual and share list or library or folder with everyone. Yes, we would need to develop automation that can help manage the scale. But that’s a worthwhile trade-off for reducing oversharing!

More to consider

Large Custom Security Groups

There might be Large Custom Security Groups in tenant. What if the user wants to share site with one of these Large Custom Security Groups? What kind of site that would be? Private? Public?

Consider the following. When a team owner adds a security group to team members – it’s not a group added, but individual users. That makes sense – all team members can clearly see who are the other team members. That makes the team private. Private team should not be additionally shared at SharePoint site level. Only permissions should be provided through team.

Public team – as well as public standalone site – can be shared with EEEU. But what if the requirements are not to share the site with “Everyone…” but share with some other Large Custom Security Group – e.g. “All employee” or “All Central Office Users”? Can we do it? Should site be private or public in this case?
My opinion: site should be labelled as public. Site owner can request a public standalone site or create a team self-service, then site owner can remove “Everyone…” group from permissions and add a custom security group at any level.

Some orgs choose to recommend providing access to the standalone SharePoint sites via security groups vs SharePoint groups. So it is possible we have a private standalone site with access provided to security group (or m365 group). This is where an or should have their own policy – how big the group should be to be considered as large group and trigger site label as public. There are also dynamic security groups.

Automation Requirements

To support this model, we’ll need (at least) the following custom-designed solutions:

  • Automated Site Provisioning: A request-and-approval process for creating labeled standalone sites.
  • Channel Monitoring: A custom solution to detect and flag private/shared channels under public Teams, since there’s no out-of-the-box enforcement.
  • Large Custom Security Groups Monitoring: make a list of large custom security groups users can share information with – and check on scheduled bases – if the site is shared with large custom security group – site must be labelled as public.
  • Sharing site with “Everyone except external users” : If user accidentally removes “Everyone except external users” from public site – there must be an option for user to add “Everyone except external users” with permissions Read or Edit. Site can be shared with “Everyone except external users” only at the root site level and only if site labelled as Public.

Environment Clean-Up

To prevent oversharing, we should not only “from now on” follow the strategy described above, but also make sure our existing sites are compliant with our governance. This would be another challenge.

References

SharePoint Inactive Site Policies Deep Dive

SharePoint Advanced Management includes Inactive Site Policies under Site lifecycle management. Effective content lifecycle management is a key pillar of SharePoint governance. It plays a vital role in optimizing storage, preserving data integrity, and ensuring regulatory compliance. By systematically removing inactive or outdated sites, it also enhances security. Additionally, it supports successful Copilot implementation by ensuring that the information accessed is both accurate and current. So, how exactly this Inactive site policy works and what is the difference between Entra Id groups expiration policy and SharePoint Inactive Site Policy.

SharePoint Inactive Site Policy vs m365 Groups Expiration Policy

The Groups Expiration Policy has been a feature of Azure AD (Entra ID) for quite some time. It is included at no additional cost. This policy automatically notifies group owners about upcoming expirations and provides options to renew or delete the group. Since all self-created Teams teams and Viva Engage communities are backed by SharePoint sites and managed through Microsoft 365 Groups, this policy also plays a significant role in SharePoint governance ensuring that information stored in SharePoint remains current and properly maintained. I have an article Microsoft 365 group expiration policy deep dive.

Inactive Site Policy is a feature of SharePoint Advanced Management (SAM), which is an add-on and require premium SharePoint license. It also Identifies inactive sites, Sends notifications to site owners and can automatically archive or make sites read-only. Sound like very similar to to groups expiration policy.

Key differences

Inactive site policy user experience

Here is how the email notification looks like:

Note that

The email subject includes “Action required” and site title (name).
It always says “… has been inactive for more than a month” even if the policy configured for “6 months”.
It shows SharePoint logo, which might mislead “teams-oriented” users.
Site title is not clickable, so site admin/owner cannot just click site link but have to navigate to site manually.
When user clicks button “Certify site” – a message “The action completed successfully” pops up at the bottom of the email for a few seconds and then disappears. The email itself does not change, so when a user opens the same email again – there is no visual evidences the action was taken.

At the bottom of the email Microsoft mentions tenant name.

The email template is the same for all kinds of policies – it does not matter if the policy action is configured configured as “do nothing”, or to automatically enforce archive site or set it to read-only. I.e. email just says “Select Certify site to confirm if it’s still in use, or consider deleting it if the site is no longer needed.”. Email does not inform users that site will be set to read-only or archived.

Also there is no link where a user can get more info on the subject, but Microsoft says that inactive sites policy email template will be customizable – in the Site lifecycle management policies v2 expected summer 2025.

Admin – Inactive sites report

You can download a csv report of inactive sites generated by policy.
Report includes fields:
Site name, URL, Template, Connected to Teams, Sensitivity label, Retention Policy, Site lock state, Last activity date (UTC), Site creation date (UTC), Storage used (GB), Number of site owners, Email address of site owners, Number of site admins, Email address of site admins, Action status, Total notifications count, Action taken on (UTC), Duration in Read-Only.

There is no GUI to see the list of inactive sites (you can only download a csv file), but there is a magic button “Get AI insights”.

Get AI insights

Here are insights I have seen so far:

  • Inactive sites with significant storage usage
  • Multiple sites owned by the same account
  • Sites with Multiple Owners
  • Sites inactive for over a year

Inactive sites policy behavior

Policy sends emails immediately after policy activation. That means if you have thousands of inactive sites you might hit a 10k exchange limit of daily emails sent.

If a user owns multiple inactive sites – he/she will get multiple emails.

You can scope the policy down by site template, sensitivity label and creation source if you want different behavior for different types of sites, e.g. if you want to setup longer period of inactivity for one type of sites and shorter for others… not sure when it makes sense…

Implementing an Inactive sites policy

First of all – It is highly recommended to take care of ownerless sites (find owners) before triggering an Inactive sites policy.

If you have a relatively new tenant – you probably have not much inactive sites, so turning the policy on should not be a problem. The older your tenant is the more inactive sites you have. For older tenants you probably already have a lot of inactive sites – ant that could be a problem. So we’d need to take care of initial policy implementation, and after some time it will just work so we could forget about it.

There is no way to pilot this policy with pre-selected scope of sites or users. You can scope the policy down by site template, sensitivity label and creation source, but you cannot scope the policy down the way only sites or uses you want to be a testers or pilot project members will be the target of the policy.

In small orgs there should be no problems implementing this policy. Still I would start from just getting a report. There is a “How long after the last activity should a site be considered inactive?” configuration, so I’d start from the longest – 6 months, then move to the shortest you need. Medium orgs could get some ideas from recommendations to large orgs below.

In large orgs you might

  • trigger a spike in number of tickets submitted by users who needs help
  • hit a maximum sending limit with Exchange Online which is 10,000 email recipients per day

So it would be crucial for enterprises to avoid an initial surge and start from smaller number of recipients, and gradually let the policy work at a full strength. One of the options to achieve that would be

  1. configure the policy for reports only, get inactive sites report
  2. select sites owner and admins in a separate list – then select only unique ones – so every user will get only one email, split this list into small chunks
  3. communicate to site owners (by chunks) – using enterprise-approved “send from” email and enterprise-branded email template saying that the policy is gonna be implemented, you might receive an email (like this one – screenshot), you can trust this email and click buttons. A list of site urls user owns must be included in the email, so user could visit these sites
    (Optionally) you can instruct users how they can delete sites if site is no longer needed or archive sites if they are not sure if it is still needed or not

If so – it’d

  • forewarn users so they would know to do and not be surprised and would create less tickets
  • users might choose to delete or archive sites which would also
  • users would visit their inactive sites and trigger sites activity, and that should dramatically decrease number of emails sent to users initially, on the day one of policy implementation
    ideally – if users visit all sites – you’d have no inactive sites, so you’d just turn the policy on with no fear

then you’d wait for a couple of weeks, get new report to ensure that you have much less inactive sites – and you’d just enable the inactive sites policy (starting from the longest period – 6 month of inactivity)

References