Tag Archives: Ownerless groups

Ownerless Microsoft 365 groups policy staged implementation in large environments

Usually, a Microsoft 365 group can be created by anyone in your organization as part of creating a Team, a Yammer community, an Outlook group, a SharePoint site, etc. If the group owner leaves the company and the account gets deleted, the group becomes ownerless.

It would be a nightmare to reach out to ownerless group members one by one, trying to figure out who is the actual data owner and who should become the group owner. So we need some kind of automated solution.

There is a Microsoft ownerless groups policy that detects ownerless groups and sends emails to the most active group members, asking if they want to become group owners. If a member accepts ownership, the policy automatically elevates that person from group member to group owner. The policy does not cover standalone SharePoint sites, but the majority of orphaned resources in an organization are usually Microsoft 365 groups, so this policy should still help a lot.

The policy was designed with the idea of preventing ownerless groups, meaning it handles them gradually over time as they become ownerless. Because of that, it’s recommended to activate the policy as soon as you set up the tenant. Configuration is done through the GUI, and it’s intuitive and straightforward. Microsoft documented it well, but if you still have questions about how the policy behaves, here is my Q&A covering what is not included in Microsoft’s FAQ, along with some tips, tricks, and gotchas.

The problem is that Microsoft introduced this feature relatively recently, and if you’ve owned your tenant for years, you probably already have some ownerless groups. In small or medium environments with a few dozen ownerless groups, this isn’t a big issue. But in a large Microsoft 365 or SharePoint Online environment, you might end up with hundreds or even thousands of ownerless (or orphaned) resources that you have to deal with.

One of the challenges is how to implement the policy correctly when you already have many ownerless groups, and then how to manage the groups that will become ownerless in the future. In other words, we need to solve two consecutive issues:

  • Remediate vast amount of existing ownerless groups
  • Prevent groups to become ownerless

Obviously we’d need two different strategies and policies configurations.

There are also 3-rd party tools – like SysKit Point that can help with orphaned resources by enforcing minimum number of owners. There is also “Orphaned resources” policy under SysKit that allows multiple workflow options to resolve the issue – but there is no “fully automated” option -all SysKit options require an interaction from admin/manager.

Microsoft 365 built-in feature – “Ownerless groups policy” allows fully automated process:

  • detects ownerless groups, and for every group found
  • generate e-mail invitations to most active group members
  • assigns users as group owners if they accept invitation

Another problem in large environments is that we have strict requirements we need to satisfy:

  • end-users to get a limited number of emails in a certain period so they can process
  • end-users get only relevant messages so they will not ignore further notifications
  • high percentage of acceptance and (ideally) no orphaned resources

We want the policy to be piloted or tested in production against a small group and then we want phased implementation – so we could have a chance to get a feedback on phase 1 and adjust our approach at phase 2 etc.

The policy allows limiting the policy scope in two ways:

  • by limiting “who can receive” messages – it’s done by specifying a security group – so only this security group members will be eligible to get invitation and accept or decline it
  • by limiting Microsoft 365 groups that would be in scope for the policy – it’s done by specifying group names

Two options can be specified in the same policy and effective eligible members would be those who satisfy both requirements.

Configuration is done using GUI – i.e. there is no PowerShell commands known on the subject at the moment.

There are a lot of “what if” questions regarding the policy – most of them are resolved in Microsoft’s “Microsoft 365 ownerless group policy FAQ” and my Ownerless m365 groups Q&As, gotchas, findings…

But the most important gotcha for me is that we cannot reconfigure the policy or reactivate it to trigger additional messages for groups that already had messages generated earlier. In other words, if email notifications were already sent for a group and the policy stopped working after the defined time period, it’s done for good. No more emails can be generated for that same group.

The other limit is you can only specify no more than 50 Microsoft 365 groups in policy under “Apply policy to Specific groups” option. And we’d keep in mind exchange’s limit of 10,000 emals per account per day.

So, having this said, what would be the proper approach to do phased implementation in terms of configuring policy to scope it down for each step?

First – know your data. Get full report on ownerless groups, analyze it and come up with approach. Let’s assume we have an org with ~100K users and ~5000 ownerless groups. I bet you will find out that you have

  • large m365 groups (100+ members): <1%, i.e. 10-20 groups
  • medium m365 groups (10-100 members): ~25%, i.e. ~1000-2000 groups
  • small m365 groups (1-10 members): ~50%, i.e. ~2500 groups
  • null m365 groups (0 members): ~25%, i.e. ~1000-2000 groups

You’d might have your own classification, but I would propose the following approach to each category.

  • large groups:
    configure policy with “Apply policy to Specific groups” option
    and specify all or several of your large groups (the limit if 50 allowed groups in this field)
  • medium groups:
    configure policy not scoped down (e.g. apply to all groups, all users)
  • small groups:
    skip the policy, use PowerShell to elevate all group members to owners
    optionally – elevate specific titles (manager, lead) or salary grade members to owners
  • null groups:
    consider deleting these groups
    optionally – delete only inactive no-members groups or groups with no or small amount of storage/files.

You’d also come up with the ideas on

  • desired min and max number of owners
  • deleting groups/sites phased approach
  • archiving groups/teams/sites

Remember – this is production, so at this moment you should test the policy in non-prod an be fully comfortable with all aspects of configuring the policy and formatting e-mail template etc.

As a remediation part plan I would propose the following:

Wave 0 – piloting

select a few (3-5) ownerless m365 groups, preferably your colleagues from IT – whose members will be your pilot team, so you could finalize all settings and polish notification message etc.

Implement the policy with settings:
– All active members, 5 members to notify, 2 weeks
– Sender
– Subject and message – clean-up oriented
– Specified groups – select these pilot groups

In parallel, while you are waiting weeks for the policy to pause, start developing PowerShell scripts that will 1) delete null (no members) groups and 2) elevate members to owners (get how many members can be elevated if elevate only certain members)

Track user’s response – % of declines and accepts

Get feedback from users – how well the notification message is understandable etc.

Wave 1 – large groups and small groups

Implement the policy for large with settings:
– All active members, 5 members to notify, 5 weeks
– Sender – specially created m365 group with the name you need as sender
– Subject and message (polished at wave 0, clean-up oriented)
– Specified groups – select large groups

For small groups – run PowerShell script that elevates members to owners.

Wave 2 – medium groups and null groups

For null groups – run PowerShell script that removes groups with no owners and no members (optionally only inactive groups and/or no content groups).

At this moment number of ownerless groups should be decreased significantly. So we should be good to start implementing policy for all groups. But we are getting new ownerless groups permanently – during all the waves of policy implementation.

Get the report again. In case you have e.g. up to 2,000 orphan groups – you can reconfigure policy and “Apply this policy to” All groups.

If you have more than 2k ownerless groups left – consider the following: create a few service accounts in Entra ID. Add these account to ownerless groups as owners (distribute equally). That’d make groups not ownerless. Then you’d configure the policy. Than delete these service accounts from entra id one by one, so it’d make groups ownerless again, but not all at once, but gradually.

Wave 3 – all groups left ownerless

After a few months you configured ownerless groups policy for all groups – get reports on your orphan groups again – there should be some % of remediated groups, and some % of groups that are still ownerless after all notifications sent to most active members (nobody volunteered to be a group owner). But you still need to deal with these ownerless groups. Consider the following approach based on groups activity (this would require PowerShell):

  • active groups – elevate most active members to owners
  • groups with no recent activities – rename group, remove all members, configure “request access” email and let the group stay for a few more months/years – then delete groups not reclaimed

Wave 4 – permanent policy and custom deletion

After you completed clean-up (policy + your custom solution), consider policy re-configuration.
Specifically, you might want to update the notification Subject and Message.

Questions and Answers

Q: Isn’t it a security risk if we elevate members to owners? Would a member get access to more information that he/she did have access to before.
A:
1) Elevating members is the same risk as implementing the ownerless policy, as policy does the same – it elevates member to group owner.
2) When a member is elevated to group owner – a member does not get access to more information, as
a) for standard channels – he/she did have access as a member
b) private channels stays private – new group owner does not get access to private channels automatically
c) shared channels stays with the same permissions also
References

Ownerless Microsoft 365 groups, teams and sites Q&A

Every resource under Microsoft 365 (Microsoft Teams team, Microsoft 365 group or SharePoint site) must have an owner/owners. Otherwise to whom we communicate on any question – site/group permissions, membership, site/group/team retention policy, content classification etc. Who will be responsible for team/site/group content and configuration and who will provide access to this site for other users.

NB. This article is about ownerless groups policy. There is a new (released 6.3.2025) “Site Ownership Policies” that can work against standalone sites.

MS: A team in Microsoft Teams or a Microsoft 365 group and its related services can become ownerless if an owner’s account is deleted or disabled in Microsoft 365. Groups and teams require an owner to add or remove members and change group settings.

Recently Microsoft implemented a new feature: a policy that automatically asks the most active members of an ownerless group or team if they’ll accept ownership. Very important feature. TY Microsoft!

It is important because many other “governance” activities (e.g. permissions attestation, retention policies) rely on site/team ownership. I.e., before we notify site owner that the site is going to be deleted due to inactivity – we want an owner present.

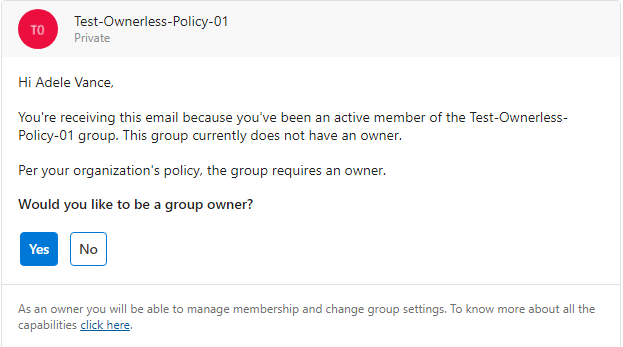
That is how the out-of-the-box notification email looks like:

The configuration via wizard is straightforward and intuitive, and Microsoft documented it well, but still we have some questions regarding the policy behavior.

Q: Is it about groups ownership or sites ownership?
A: Group ownership and group-based sites ownership (teams, yammer etc.). Non-group based aka Standalone sites (e.g. communication) are not in scope of this feature/policy.
Upd (June 2025): Microsoft released a new SharePoint “Site Ownership Policies” that works against standalone sites.

Q: Who can configure this policy? What kind of permissions required to create/update policy?
A: Microsoft says “Manage Microsoft 365 groups” permissions required – e.g. admins with Global admin or Groups Admin roles required. “Teams administrator” or “SharePoint Administrator” cannot configure the policy.

Q: After the policy activated – who will receive notification? What exactly “most active members” mean?
A: Microsoft only says “most active members” and does not disclose specific algorithm behind.

Q: How about group with no members? What if somebody created a group but did not add any members and then left?
A: In this case the policy will not work – as there is nobody who can be notified. These kind of groups must be handled manually, because having no owners or members does not mean that nobody uses the related SharePoint site. What if the group is public and hosts some valuable data?

Q: How do we know the group is ownerless? Only if owner has been deleted from AAD? What if an owner is just blocked or became unlicensed?
A: For the policy Microsoft consider blocked or unlicensed users presented in the group owners list as valid users and still group owners; so the policy will not be triggered until the group owners list is empty.

Q: We have implemented Azure AD Settings “EnableGroupCreation” and “GroupCreationAllowedGroupId” (as per Microsoft: Manage who can create Microsoft 365 Groups), so not everyone can create m365 groups. Would this impact the ownerless groups policy? In other words – if a user cannot create group – would this keep user from being assigned as a group owners?
A: No. Microsoft’s Manage who can create Microsoft 365 Groups trick regulates groups creation only. Later – when a group is created – nothing prevents such user to be added as a group owner.

Q: I support a large Microsoft 365 environment and we already have hundreds and thousands of ownerless groups. I’m concerned how users might react and whether our helpdesk support teams are ready for new type of tickets etc. Implementing the policy in test/stage environment does not make much sense, since there are no really active users etc. So, can I test this policy in production – on real users, but pilot it within a small number of users or ownerless groups before applying to all groups in the environment.
A: Yes, you can do a test or pilot implementation in production limiting the impacted users or groups.
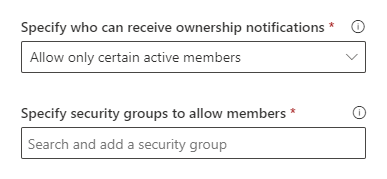
– if you need to limit users who will be getting notifications – e.g. a “pilot team” – during Step 1 “Notification Options” under “Specify who can receive ownership notifications” you can select “Allow only certain active members” and under “Specify security groups to ‎allow members‎” you can select a security group – so only members from the specified security group will be sent ownership request. Microsoft 365 groups do not work here.

however – if you choose this option – it is possible that Microsoft 365 groups might have more active members who are not the security group members. E.g. it might make sense to use this option for piloting – against a small number of isolated set of groups/members, but for not for phased implementation. If you have some specific requirements for group ownership – e.g. “only managers could be group owners” or “contractors cannot be group owners” – using security group to limit potential group owners would make sense.

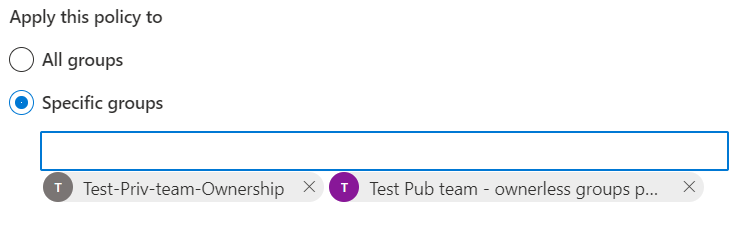
Another option you can use for phased implementation or piloting the policy is to scope it down to a several selected m365 groups – use “Apply policy to” – “Specific groups” option:

NB! After all notifications are sent for a group – you will never ever get any more notifications for the same group. Even if you re-activate the policy or change policy parameters or whatever – it will not help. Once messages sent – it’s done for the group forever.

NB: Please also check “Microsoft ownerless groups policy in large environment“

Q: How many groups I can specify if I select Apply policy to Specific groups option? Is there a maximum?
A: Yes, there is a limit. You can specify no more than 50 groups.

Q: I know the policy is applied to Microsoft 365 groups only. But I have many standalone sites with no owners (no site collection administrators). How do I deal with ownerless SharePoint sites?
A: Options are: manual intervention, PowerShell, 3-rd party tools – depending on your specific case. E.g. you can elevate some “Site Owners” SharePoint group members to site administrators. For modern sites – how about converting standalone sites to Microsoft 365 group-based sites (TBC – as at the moment it is not clear if it is possible)?

Q: What happens after one of the notified members accepts the ownership request?
A: No more notifications will be sent for this group. But previously sent notifications will still be valid.

Q: What happens if several of the notified members accepts the ownership request?
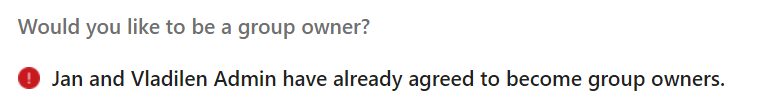
A: Only two first served basis. As per Microsoft, only two members can be assigned to group owners via the policy. When a group got two owners – invitation message actionable item for the rest will be converted from “Would you like to be a group owner?” to “MemberName1 and MemberName2 have already agreed to become group owners.” with no “Yes” and “No” actionable buttons.

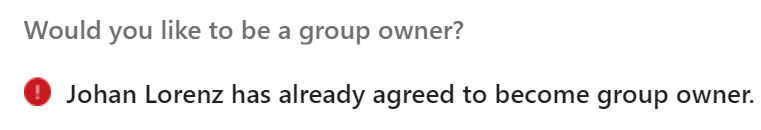
NB!
I have tested the policy one more time, and this time after first member accepted ownership – no other members were able to accept ownership. They got a message “Johan Lorenz has already agreed to become group owner”:

@Microsoft, any comments?

Q: What if admin assign owner to group?
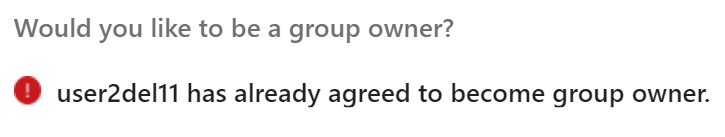
A: The group becomes not ownerless. Notification messages will not display invitation to become an owner anymore, and instead of “Would you like to be a group owner? – Yes or No buttons” it will be shown as “username has already agreed to become group owner.”:

Q: Can I customize an ownership notification?
A: Yes, but
– E-mail message body is limited to ~1040 characters
– Policy does not provide any WYSIWYG rich text format options (but there are some tricks you can use to format it with headers, bold/italic, links, bullets/lists: more on email template format.)

Q: Can I use shared mailbox or security group or distribution list as a “send from” e-mail account?
A: No. You can use only user or m365 group mailbox.

Q: Should “send from” user e-mail account be licensed with Exchange?
A: TBD (but most likely no).

Q: What if a group become ownerless after policy is activated?
A: Policy detects the group is ownerless and start sending notifications within 24 hour.
Actually the policy was designed to prevent ownerless groups. So it is recommended to activate the policy once you get the tenant.

Q: We know, that if a user declined ownership once – he will not get any more emails on the same. Is that true for current policy or for any further policies activations? I.e. If the policy updated/re-activated – will it remember user’s decision or it all starts from scratch?
A: TBD
All the next incarnations of the policy will not trigger e-mail notification for the group if all notifications were sent earlier. I.e. in this case user will not receive any more notifications on the same group.

Q: If a user declines ownership – does that mean that someone else will start receiving emails so that the configured number of active members is maintained? What if all “active members” choose “No” at week 1 – will the policy select other members or what?
A: No. The policy will send notification to other initially selected members.

Q: If nobody accepted ownership – can we reconfigure the policy to sent more notifications – e.g. to wider range of active members or with more strict language in an e-mail template?
A: Yes and No.
Yes – if you e.g. specified 2 members and 6 weeks in the policy, and then after 3 weeks you want to increase number of members to notify to 10. But (it seems like it’s a bug) you have to deactivate the policy and activate it again with new parameters.
No – if the policy’s specified number of notifications is expired. I.e. if all emails supposed to be sent are sent – no more emails will be generated for this group, even if you reconfigure or deactivate/activate the policy, so the group active members will not get any more notifications on the same group. Workaround: you can add a dummy account to group owners and then delete this dummy account from AAD, so groups become normal and then ownerless again.

Q: What if we specify emails should be sent for 5 weeks, but stop the policy after two weeks? And then we re-activate the policy.
A: It is expected the policy will continue sending e-mail notifications until 5 emails sent.

Q: What if we specify 3 weeks in policy, but then re-configure the policy with 5 weeks specified and activate it again?
A: tbc – not tested yet

Q: Is there a difference in the policy behavior when we reconfigure the policy or deactivate and then reconfigure the policy?
A: Yes, at least – what I noticed so far:
To update number of members to notify – if you just reconfig the policy – it pics up update but acts like there was no updates. So to actually update number of members to notify you need to deactivate the policy and activate it again with new parameters.

Q: What if we have more than 10,000 notifications to send? Will the policy drop some of them or all notifications will be send but next day?
A: tbc – not tested yet

Q: Let say we have an ownerless group with 20 members. Let say we specified security group to limit user who will get invitations. And this security group includes only 6 users from the orphan group out of total 20. Microsoft says the policy will select the most active users. So the question is: will the policy select the most active users from the 20 orphaned group users and if the user in the security group – he/she will get an email?
A: No. The policy will select the most active users only from these 6 users that included in the security group, ignoring 14 users, even if they were more active then these 6 selected.

Q: What happens after the policy expires? E.g. after all notifications are sent…
A: Policy does not expire. If the policy is activated – it works. If all notifications are sent for the group – so yes, policy is done for this group. But if a new group became ownerless – policy will be triggered for this group again.

Q: If all the notifications are sent for the group – what are admin options to activate ownerless groups policy against this group?
A: There are no “legal” options, but there is a workaround. You can add an owner to the group and then delete this account – so this way you make the group ownerless again – and the process would start from scratch, as for the policy this group will be a new ownerless group.

Some more findings:

User can forward invitation message, but recipient who is not a selected group member – will not see actionable “Yes” “No” buttons. Selected Group

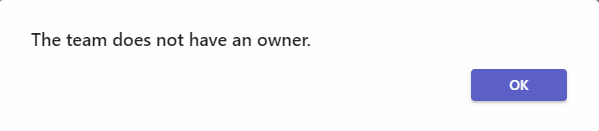
If a public group does not have an owner – all requests to joint the team will be declined with “The team does not have an owner” message:
(that means no new members, i.e. no new contributors, but read-only visitors access is still available for everyone, as group is public):

Users can go to My Groups to see groups (Teams, Yammer communities and SharePoint Sites) they are members or owners of.

Proposal to be a group owner lasts forever. So if a user after some time finds an email that asks him “Would you like to be a group owner?” and clicks Yes – he/she will be a group owner, even if the policy is already updated or removed.

As per Microsoft, only first two members can accept the ownership of an ownerless group. No additional members are allowed to accept ownership. If either one or two members accept ownership, other members won’t receive further notifications.

Re-create (or re-activate) the ownerless group policy

You can de-activate the policy and then activate it again. Or you can reconfigure the policy. If you activated the policy again (or re-configured it), but emails are not sent – this might be an expected behavior. Let say you initially specified 3 weeks and 3 notification were sent to the most active ownerless groups members. That means no more emails will be generated for these groups.

De-activate the ownerless group policy

Just uncheck “When there’s no owner…”, and save it to stop the policy:

downside – you’d need to configure the policy from scratch – all previous settings are gone now


Track the ownerless group policy in action via Audit Log

How do I, as an Microsoft 365 administrator, know if the policy works or not, are the emails sent or not and how many (if any) users are accepted “Would you like to be a group owner?” invitation?

Microsoft 365 Audit Search under Microsoft Purview (Compliance center) should help.

Operations:

  • OwnerlessGroupNotified – “Notified ownerless group”
  • OwnerlessGroupNotificationResponse – “Responded to ownerless group notification”
  • OwnerlessGroupNeedAttention – “Unattended ownerless group”

OwnerlessGroupNotified – “Notified ownerless group”

(No-brainer) – means that the policy sent e-mail notification to some of the group members. Under “Members” property you can see list of notified users, and under ExtendedProperties – “FirstNotificationDate” and “NotificationChannel” (usually “Outlook”)

OwnerlessGroupNotificationResponse – “Responded to ownerless group notification”

Could have “ResponseType” as “AcceptOwnership” or “DeclineOwnership” under ExtendedProperties, as well as “OwnerCount”.

OwnerlessGroupNeedAttention – “Unattended ownerless group”

indicates all notifications are sent and the group is still ownerless. In the event details you’ll find under ExtendedProperties:

{
    "Name": "FirstNotificationDate",
    "Value": "05/04/2023 13:46:07"
},
{
    "Name": "LastNotificationDate",
    "Value": "05/11/2023 14:28:21"
},
...

UserId: OwnerlessGroupComplianceAssistant

Record Type (AuditLogRecordType): 126

It seems like event is not added to the Audit log when a policy is created or updated.

Who can create Microsoft 365 Groups

It is possible to limit users – who can create Microsoft 365 Groups (please refer to Microsoft: Manage who can create Microsoft 365 Groups – there is a guide and PowerShell code sample). This might help to keep the environment under control – let say, “only managers can create groups”, or “contractor should not be able to create teams”.

Azure AD Directory Setting “GroupCreationAllowedGroupId” works only for creation. Later, when the group is create – it is possible to add to group as a group owner those who is not able to create group. But, if you want your tenant configuration consistent in terms “if a user cannot create a group – user cannot be a group owner” – consider using the same security group in policy’s notofication options “Specify who can recieve ownership notifications”

Issues

“Ownerless group policy configuration failed” error message.

And “Failure in configuring ownerless groups policy” and “Please try again.”
– seems like a permissions issue.
SharePoint admin, Teams admin or Group admin roles: cannot configure Ownerless Groups Policy.
Global admin: yes, can configure Ownerless Microsoft 365 Groups Policy.
What is the minimum role required?
According to a recent update of the Microsoft’s article – “A Global administrator can create a policy…”. In my experience – groups admin can also configure the policy.

The remote endpoint returned an error (HTTP ‘500’). Please try again later

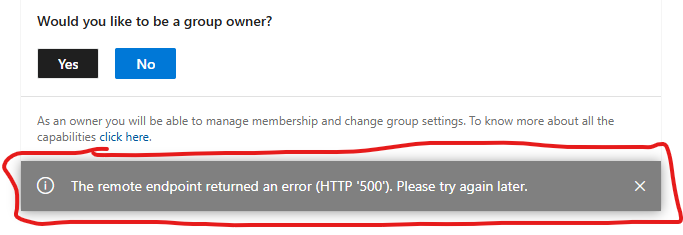
When a user clicks on a button “Yes” or “No” in a notification email, a message “The remote endpoint returned an error (HTTP ‘500’). Please try again later.” pops up:

The remote endpoint returned an error (HTTP '500'). Please try again later.

We are unable to complete that action right now

Since around Feb 5 2025 users who want to accept group ownership and click Yes – get an error message “We are unable to complete that action right now.Please try again later.”
Microsoft is aware of it. Waiting for a fix.
Update: this bug was fixed by Microsoft in a few weeks/months 🙂

References